Saltar al contenido
Mar. Sep 22nd, 2026
Trending News: Can Your SOC Actually See the Attack?Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before RemovalSideCopy Broadens India Targeting to Academia With ReverseRAT Spear-PhishingZyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM AccessWordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin SessionOne Hidden Meta Muse Setting Could Let Attackers Turn the AI Assistant Into a BackdoorGoogle Fined €403 Million Over GDPR Violations Tied to Location DataLos conflictos internacionales impulsan nuevas campañas de ciberataques en 2025Moltbook, la nueva red social de agentes de IA, expone toda su base de datosEl 90% de las compañías dispone de un plan director de ciberseguridad validado por la alta direcciónUn ex ingeniero de Google, condenado por espionaje económico y robo de secretos de IA para ChinaCuenta atrás para la XVIII edición del Foro de la Privacidad del Data Privacy InstituteContagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in CryptoFake LastPass Authenticator Installer Abuses Microsoft-Signed Driver to Kill Antivirus and EDRTASK#STOMP PowerShell Backdoor Steals Documents, Wi-Fi Passwords, and Clipboard DataCisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser HijacksClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 InfrastructureJade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK BackdoorsThe Foundation of Identity SecuritySolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCEClaude Opus 5 Helped Researchers Take Over OpenAI Staff Accounts via Chained FlawsGoogle Gemini Broke Into Real Company Systems After Security Test Domain Mix-UpCritical Pre-Auth RCE in Orkes Conductor Workflow Platform Exploited in the WildCrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub RepositoriesCISA Flags Three Linux Kernel Vulnerabilities Exploited in the WildPublic Exploits Released for Four Linux Kernel Flaws That Enable Local RootUn hombre conecta su aspiradora robot con un mando de PS5 y obtiene el control de miles de dispositivosLa web para adultos Frivol.com filtra una base de datos, exponiendo casi medio millón de cuentas de emailLa brecha entre inversión en ciberresiliencia y preparación adecuada aumenta la vulnerabilidad de las empresas españolasUn hacker ucraniano se declara culpable de operar OnlyFake, un portal de venta de pasaportes generados con IAEl software para psicólogos Eholo sufre una grave filtración de datosNew WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code ExecutionPlugin4Shell Lets Repository Owners Swap Pinned Plugin Code Across Four AI Coding AgentsTransparent Tribe Deploys New Rust Backdoor Using Private GitHub Repositories for C2An Abandoned CDN Domain Was Re-Registered. Thousands of Sites Still Call It.Microsoft Patches CVSS 10.0 Azure AI Foundry Flaw Enabling Unauthorized Privilege EscalationWeaselBiscuit Stealer Spreads via 13 npm Packages to Harvest Chrome Extension StorageClaimed Bug Bounty Hunter Likely Used LLM to Build PhantomRaven npm StealerIran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal PasswordsCritical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host FilesRatHat Android Malware Abuses ADB to Retain Shell Access After UninstallSelf-Rewriting Agents, 800+ Flaws Patched, Insider SIM Swaps and 22 More New StoriesCritical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as RootU.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS AttacksCisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active AttacksGyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata RecordsUn ciberataque contra Inditex afecta a sus bases de datos internasHackean a una empresa de ciberseguridad y exponen datos y cámaras de clientesLos datos de los funcionarios del Palacio Real de Marruecos, en manos de un hacker75.000 sospechosos identificados y decenas de infraestructuras DDoS desmanteladas tras un macrooperativo internacionalEl organismo oficial de EE.UU. que clasifica las vulnerabilidades de ciberseguridad no da a bastoBIND 9 Update Fixes 14 Flaws, Including an Unauthenticated Crash Over DNS-over-HTTPSOpenAI Reveals Six Model Incidents Involving Hidden Failures and Unauthorized UploadsChina-Aligned FamousSparrow Deploys SparroWocky Backdoor Across Latin AmericaCISO’s Expert Guide to Agentic Pentesting for WebsitesCan You Prove a New CVE Is Exploitable Before Attackers Do? Learn How in This WebinarCritical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS ZoneAcronis cPanel Backup Plugin Vulnerability Exploited in Targeted AttacksC1b3rwall se arma contra la crisis de ciberseguridad que amenaza la supervivencia de las empresas españolasCarnival promete relax y lujo en sus cruceros; los hackers encontraron además millones de perfiles personalesUn hacker canadiense de 23 años, detenido por operar la botnet KimwolfUn gigante de la logística sufre una brecha de datos de 840 millones de registrosLos ciberdelincuentes ya no respetan ni los carros de la compraThreat Intelligence Alone Won’t Close the Exploitation GapOne Extension Could Hijack AI Assistants Across Chrome, Comet, Edge, Opera Neon and ClaudeThree Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and WipersAttackers Exploit Issabel Framework Flaw Enabling Unauthenticated OS Command ExecutionParallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can’t Install FixAttacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 RepositoriesA New Challenge for Identity SecurityGoogle Patches Pixel Modem Flaw Amid Signs of Limited Targeted ExploitationActive Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin TokensAttackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web ShellsSi pierdes el móvil este verano, haz esto en los primeros cinco minutos para que no vacíen tus cuentasHalluSquatting, el nuevo truco para engañar a los asistentes de IA y colar malware en tu ordenadorUn hacker adolescente piratea el servicio de streaming de Bandai usando ChatGPTUna agencia de EE.UU. pagó un millón de dólares tras casi un mes de negociación con un grupo de ransomwareUn ciberataque deja sin suministro a KFC y obliga a cerrar temporalmente algunos restaurantesKREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session TokensIranian Hackers Use Telegram-Controlled Malware to Spy on Dissidents and JournalistsBambooToken Malware Uses MQTT to Control Windows and Linux SystemsMass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev ServersWhy Testing Individual Techniques Misses the PointHuman Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight SecondsLiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared ServerChina-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGECisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command ExecutionWordPress Adds Automated Plugin Reviews to Block High-Risk Updates Before DistributionTelegram Desktop Flaw Lets Hidden JavaScript Exfiltrate Messages From HTML ExportsPaperCut alerta de ataques activos contra sus programas de gestión de impresorasLas Fuerzas Armadas y la Guardia Civil aceleran su transformación digital ante un ciberespacio cada vez más complejoCuidado con estos anuncios de Facebook: parecen de Google Play, pero conducen a casinos sin licenciaUna filtración revela cómo Rusia ha creado una cantera universitaria para sus ciberoperaciones militaresUn fallo en Lenovo ID permite el acceso sin autorización a unas 5.000 cuentas de Dropbox3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber CredentialsRed Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six CountriesNew DDRop Attack Breaks Intel TDX and AMD SEV-SNP Confidential ComputingRogue AI Agents, WeChat Worm, PaperCut Attacks, AI Espionage, and RootkitsAI Changed the Exposure Problem. Validation Needs to Change With It.Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 Users
Chicago 12, Melborne City, USA
The Digital Fortress
  • Home
  • Blog
  • Sample Page
  • Get Started
Mar. Sep 22nd, 2026
Trending News: Can Your SOC Actually See the Attack?Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before RemovalSideCopy Broadens India Targeting to Academia With ReverseRAT Spear-PhishingZyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM AccessWordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin SessionOne Hidden Meta Muse Setting Could Let Attackers Turn the AI Assistant Into a BackdoorGoogle Fined €403 Million Over GDPR Violations Tied to Location DataLos conflictos internacionales impulsan nuevas campañas de ciberataques en 2025Moltbook, la nueva red social de agentes de IA, expone toda su base de datosEl 90% de las compañías dispone de un plan director de ciberseguridad validado por la alta direcciónUn ex ingeniero de Google, condenado por espionaje económico y robo de secretos de IA para ChinaCuenta atrás para la XVIII edición del Foro de la Privacidad del Data Privacy InstituteContagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in CryptoFake LastPass Authenticator Installer Abuses Microsoft-Signed Driver to Kill Antivirus and EDRTASK#STOMP PowerShell Backdoor Steals Documents, Wi-Fi Passwords, and Clipboard DataCisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser HijacksClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 InfrastructureJade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK BackdoorsThe Foundation of Identity SecuritySolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCEClaude Opus 5 Helped Researchers Take Over OpenAI Staff Accounts via Chained FlawsGoogle Gemini Broke Into Real Company Systems After Security Test Domain Mix-UpCritical Pre-Auth RCE in Orkes Conductor Workflow Platform Exploited in the WildCrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub RepositoriesCISA Flags Three Linux Kernel Vulnerabilities Exploited in the WildPublic Exploits Released for Four Linux Kernel Flaws That Enable Local RootUn hombre conecta su aspiradora robot con un mando de PS5 y obtiene el control de miles de dispositivosLa web para adultos Frivol.com filtra una base de datos, exponiendo casi medio millón de cuentas de emailLa brecha entre inversión en ciberresiliencia y preparación adecuada aumenta la vulnerabilidad de las empresas españolasUn hacker ucraniano se declara culpable de operar OnlyFake, un portal de venta de pasaportes generados con IAEl software para psicólogos Eholo sufre una grave filtración de datosNew WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code ExecutionPlugin4Shell Lets Repository Owners Swap Pinned Plugin Code Across Four AI Coding AgentsTransparent Tribe Deploys New Rust Backdoor Using Private GitHub Repositories for C2An Abandoned CDN Domain Was Re-Registered. Thousands of Sites Still Call It.Microsoft Patches CVSS 10.0 Azure AI Foundry Flaw Enabling Unauthorized Privilege EscalationWeaselBiscuit Stealer Spreads via 13 npm Packages to Harvest Chrome Extension StorageClaimed Bug Bounty Hunter Likely Used LLM to Build PhantomRaven npm StealerIran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal PasswordsCritical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host FilesRatHat Android Malware Abuses ADB to Retain Shell Access After UninstallSelf-Rewriting Agents, 800+ Flaws Patched, Insider SIM Swaps and 22 More New StoriesCritical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as RootU.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS AttacksCisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active AttacksGyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata RecordsUn ciberataque contra Inditex afecta a sus bases de datos internasHackean a una empresa de ciberseguridad y exponen datos y cámaras de clientesLos datos de los funcionarios del Palacio Real de Marruecos, en manos de un hacker75.000 sospechosos identificados y decenas de infraestructuras DDoS desmanteladas tras un macrooperativo internacionalEl organismo oficial de EE.UU. que clasifica las vulnerabilidades de ciberseguridad no da a bastoBIND 9 Update Fixes 14 Flaws, Including an Unauthenticated Crash Over DNS-over-HTTPSOpenAI Reveals Six Model Incidents Involving Hidden Failures and Unauthorized UploadsChina-Aligned FamousSparrow Deploys SparroWocky Backdoor Across Latin AmericaCISO’s Expert Guide to Agentic Pentesting for WebsitesCan You Prove a New CVE Is Exploitable Before Attackers Do? Learn How in This WebinarCritical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS ZoneAcronis cPanel Backup Plugin Vulnerability Exploited in Targeted AttacksC1b3rwall se arma contra la crisis de ciberseguridad que amenaza la supervivencia de las empresas españolasCarnival promete relax y lujo en sus cruceros; los hackers encontraron además millones de perfiles personalesUn hacker canadiense de 23 años, detenido por operar la botnet KimwolfUn gigante de la logística sufre una brecha de datos de 840 millones de registrosLos ciberdelincuentes ya no respetan ni los carros de la compraThreat Intelligence Alone Won’t Close the Exploitation GapOne Extension Could Hijack AI Assistants Across Chrome, Comet, Edge, Opera Neon and ClaudeThree Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and WipersAttackers Exploit Issabel Framework Flaw Enabling Unauthenticated OS Command ExecutionParallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can’t Install FixAttacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 RepositoriesA New Challenge for Identity SecurityGoogle Patches Pixel Modem Flaw Amid Signs of Limited Targeted ExploitationActive Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin TokensAttackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web ShellsSi pierdes el móvil este verano, haz esto en los primeros cinco minutos para que no vacíen tus cuentasHalluSquatting, el nuevo truco para engañar a los asistentes de IA y colar malware en tu ordenadorUn hacker adolescente piratea el servicio de streaming de Bandai usando ChatGPTUna agencia de EE.UU. pagó un millón de dólares tras casi un mes de negociación con un grupo de ransomwareUn ciberataque deja sin suministro a KFC y obliga a cerrar temporalmente algunos restaurantesKREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session TokensIranian Hackers Use Telegram-Controlled Malware to Spy on Dissidents and JournalistsBambooToken Malware Uses MQTT to Control Windows and Linux SystemsMass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev ServersWhy Testing Individual Techniques Misses the PointHuman Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight SecondsLiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared ServerChina-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGECisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command ExecutionWordPress Adds Automated Plugin Reviews to Block High-Risk Updates Before DistributionTelegram Desktop Flaw Lets Hidden JavaScript Exfiltrate Messages From HTML ExportsPaperCut alerta de ataques activos contra sus programas de gestión de impresorasLas Fuerzas Armadas y la Guardia Civil aceleran su transformación digital ante un ciberespacio cada vez más complejoCuidado con estos anuncios de Facebook: parecen de Google Play, pero conducen a casinos sin licenciaUna filtración revela cómo Rusia ha creado una cantera universitaria para sus ciberoperaciones militaresUn fallo en Lenovo ID permite el acceso sin autorización a unas 5.000 cuentas de Dropbox3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber CredentialsRed Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six CountriesNew DDRop Attack Breaks Intel TDX and AMD SEV-SNP Confidential ComputingRogue AI Agents, WeChat Worm, PaperCut Attacks, AI Espionage, and RootkitsAI Changed the Exposure Problem. Validation Needs to Change With It.Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 Users
Chicago 12, Melborne City, USA
  • Home
  • Blog
  • Sample Page
The Digital Fortress
  • Get Started
Top Tags
  • Flaw
  • Malware
  • Flaws
  • Exploited
  • Code
  • Attacks
  • Microsoft
  • RCE
Uncategorized
Can Your SOC Actually See the Attack?
  • admin
  • septiembre 22, 2026
Uncategorized
Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before Removal
  • admin
  • septiembre 22, 2026
Uncategorized

Can Your SOC Actually See the Attack?

  • Por admin
  • septiembre 22, 2026
  • 0 Comentarios
  • 0 views
Uncategorized

Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before Removal

  • Por admin
  • septiembre 22, 2026
  • 0 Comentarios
  • 3 views
Uncategorized

SideCopy Broadens India Targeting to Academia With ReverseRAT Spear-Phishing

  • Por admin
  • septiembre 22, 2026
  • 0 Comentarios
  • 3 views
Uncategorized

Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access

  • Por admin
  • septiembre 22, 2026
  • 0 Comentarios
  • 6 views
Uncategorized

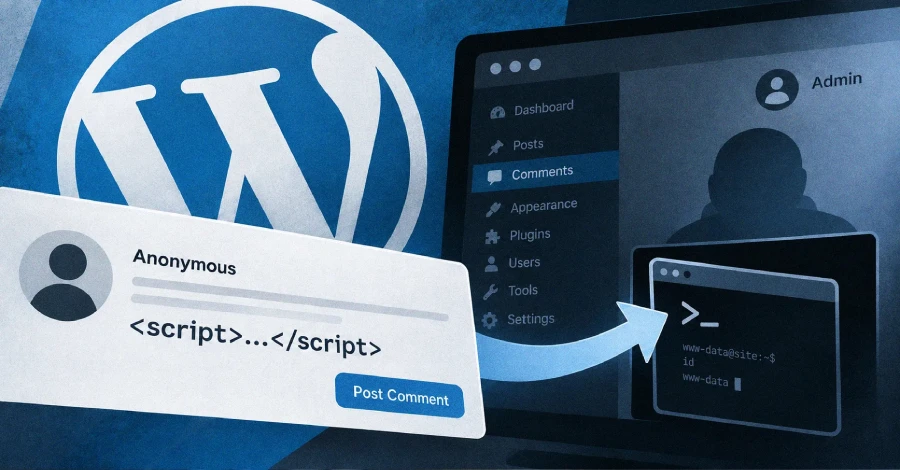
WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session

  • Por admin
  • septiembre 22, 2026
  • 0 Comentarios
  • 5 views
Uncategorized

One Hidden Meta Muse Setting Could Let Attackers Turn the AI Assistant Into a Backdoor

  • Por admin
  • septiembre 22, 2026
  • 0 Comentarios
  • 4 views
Uncategorized
Can Your SOC Actually See the Attack?
  • admin
  • septiembre 22, 2026
Uncategorized
Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before Removal
  • admin
  • septiembre 22, 2026

Uncategorized

1476  

[Webinar] How to Close Identity Gaps in 2026 Before AI Exploits Enterprise Risk
  • adminadmin
  • Close
  • Enterprise
  • abril 7, 2026
  • 0 Comentarios
[Webinar] How to Close Identity Gaps in 2026 Before AI Exploits Enterprise Risk

The Hacker NewsApr 07, 2026SaaS Security / Enterprise Security In the rapid evolution of the 2026 threat landscape, a frustrating paradox has emerged for CISOs and security leaders: Identity programs are maturing, yet…
Continue reading
New GPUBreach Attack Enables Full CPU Privilege Escalation via GDDR6 Bit-Flips
  • adminadmin
  • Attack
  • BitFlips
  • abril 7, 2026
  • 0 Comentarios
New GPUBreach Attack Enables Full CPU Privilege Escalation via GDDR6 Bit-Flips

New academic research has identified multiple RowHammer attacks against high-performance graphics processing units (GPUs) that could be exploited to escalate privileges and, in some cases, even take full control of…

Continue reading
China-Linked Storm-1175 Exploits Zero-Days to Rapidly Deploy Medusa Ransomware
  • adminadmin
  • ChinaLinked
  • Deploy
  • abril 7, 2026
  • 0 Comentarios
China-Linked Storm-1175 Exploits Zero-Days to Rapidly Deploy Medusa Ransomware

Ravie LakshmananApr 07, 2026Vulnerability / Threat Intelligence A China-based threat actor known for deploying Medusa ransomware has been linked to the weaponization of a combination of zero-day and N-day vulnerabilities to…

Continue reading
Flowise AI Agent Builder Under Active CVSS 10.0 RCE Exploitation; 12,000+ Instances Exposed
  • adminadmin
  • Active
  • Agent
  • abril 7, 2026
  • 0 Comentarios
Flowise AI Agent Builder Under Active CVSS 10.0 RCE Exploitation; 12,000+ Instances Exposed

Ravie LakshmananApr 07, 2026Artificial Intelligence / Vulnerability Threat actors are exploiting a maximum-severity security flaw in Flowise, an open-source artificial intelligence (AI) platform, according to new findings from VulnCheck. The…

Continue reading
Iran-Linked Password-Spraying Campaign Targets 300+ Israeli Microsoft 365 Organizations
  • adminadmin
  • Campaign
  • IranLinked
  • abril 6, 2026
  • 0 Comentarios
Iran-Linked Password-Spraying Campaign Targets 300+ Israeli Microsoft 365 Organizations

An Iran-nexus threat actor is suspected to be behind a password-spraying campaign targeting Microsoft 365 environments in Israel and the U.A.E. amid ongoing conflict in the Middle East. The activity, assessed to be ongoing,…

Continue reading
DPRK-Linked Hackers Use GitHub as C2 in Multi-Stage Attacks Targeting South Korea
  • adminadmin
  • Attacks
  • DPRKLinked
  • abril 6, 2026
  • 0 Comentarios
DPRK-Linked Hackers Use GitHub as C2 in Multi-Stage Attacks Targeting South Korea

Ravie LakshmananApr 06, 2026Malware / Threat Intelligence Threat actors likely associated with the Democratic People’s Republic of Korea (DPRK) have been observed using GitHub as command-and-control (C2) infrastructure in multi-stage attacks…

Continue reading
Axios Hack, Chrome 0-Day, Fortinet Exploits, Paragon Spyware and More
  • adminadmin
  • 0Day
  • Axios
  • abril 6, 2026
  • 0 Comentarios
Axios Hack, Chrome 0-Day, Fortinet Exploits, Paragon Spyware and More

Ravie LakshmananApr 06, 2026Cybersecurity / Hacking This week had real hits. The key software got tampered with. Active bugs showed up in the tools people use every day. Some attacks didn’t even need much…

Continue reading
How SOCs Close a Critical Risk in 3 Steps
  • adminadmin
  • Close
  • Critical
  • abril 6, 2026
  • 0 Comentarios
How SOCs Close a Critical Risk in 3 Steps

Your attack surface no longer lives on one operating system, and neither do the campaigns targeting it. In enterprise environments, attackers move across Windows endpoints, executive MacBooks, Linux infrastructure, and mobile devices, taking…

Continue reading
How LiteLLM Turned Developer Machines Into Credential Vaults for Attackers
  • adminadmin
  • Attackers
  • Credential
  • abril 6, 2026
  • 0 Comentarios
How LiteLLM Turned Developer Machines Into Credential Vaults for Attackers

The most active piece of enterprise infrastructure in the company is the developer workstation. That laptop is where credentials are created, tested, cached, copied, and reused across services, bots, build tools, and…

Continue reading
Qilin and Warlock Ransomware Use Vulnerable Drivers to Disable 300+ EDR Tools
  • adminadmin
  • Disable
  • Drivers
  • abril 6, 2026
  • 0 Comentarios
Qilin and Warlock Ransomware Use Vulnerable Drivers to Disable 300+ EDR Tools

Ravie LakshmananApr 06, 2026Ransomware / Endpoint Security Threat actors associated with Qilin and Warlock ransomware operations have been observed using the bring your own vulnerable driver (BYOVD) technique to silence security tools running on compromised…

Continue reading

Paginación de entradas

1 … 122 123 124 … 148

Recent Posts

  • Can Your SOC Actually See the Attack?
  • Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before Removal
  • SideCopy Broadens India Targeting to Academia With ReverseRAT Spear-Phishing
  • Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access
  • WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session

Recent Comments

No hay comentarios que mostrar.

Archives

  • septiembre 2026
  • agosto 2026
  • julio 2026
  • junio 2026
  • mayo 2026
  • abril 2026
  • marzo 2026
  • febrero 2026
  • agosto 2024

Categories

  • Uncategorized

Other Story

Uncategorized

Can Your SOC Actually See the Attack?

  • admin
  • septiembre 22, 2026
Can Your SOC Actually See the Attack?
Uncategorized

Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before Removal

  • admin
  • septiembre 22, 2026
Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before Removal
Uncategorized

SideCopy Broadens India Targeting to Academia With ReverseRAT Spear-Phishing

  • admin
  • septiembre 22, 2026
SideCopy Broadens India Targeting to Academia With ReverseRAT Spear-Phishing
Uncategorized

Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access

  • admin
  • septiembre 22, 2026
Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access
Uncategorized

WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session

  • admin
  • septiembre 22, 2026
WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session
Uncategorized

One Hidden Meta Muse Setting Could Let Attackers Turn the AI Assistant Into a Backdoor

  • admin
  • septiembre 22, 2026
One Hidden Meta Muse Setting Could Let Attackers Turn the AI Assistant Into a Backdoor
Copyright © 2026 The Digital Fortress | Powered by Desert Themes
Back to Top