 admin
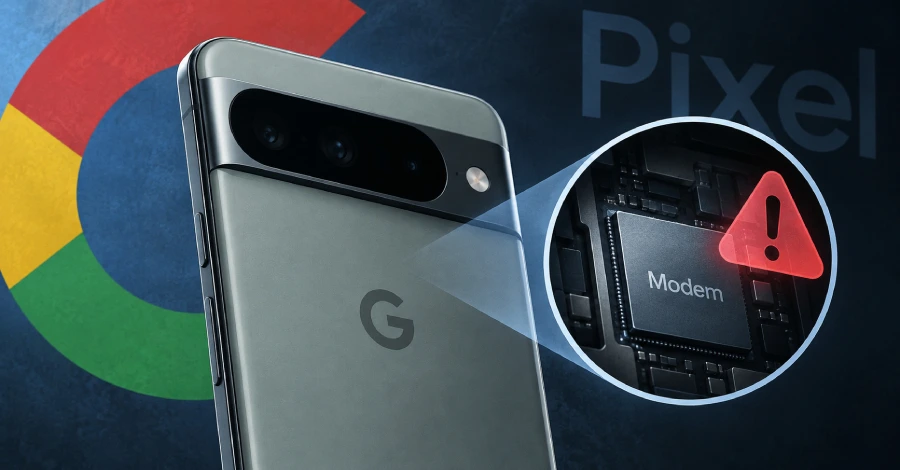
Google has disclosed that a high-severity security flaw in its Pixel Cellular Modem has come under exploitation in the wild.
The vulnerability, tracked as CVE-2026-58704 (CVSS score: 8.0), is a privilege escalation flaw.
«In Cellular Modem, there is a possible permission bypass due to a logic error in the code,» according to a description of the bug in the NIST National Vulnerability Database (NVD). «This could lead to remote (proximal/adjacent) escalation of privilege with no additional execution privileges needed. User interaction is not needed for exploitation.»
In an advisory issued Tuesday, Google acknowledged that it has found indications that «CVE-2026-58704 may be under limited, targeted exploitation» but stopped short of sharing any further details surrounding the nature of the attacks exploiting it, as well as the identity of the threat actor behind them.

Besides CVE-2026-58704, Google has addressed 109 other security flaws as part of the latest Pixel updates for September 2026. Of these, 88 allow privilege escalation, 10 allow information disclosure, nine allow remote code execution, and two allow denial-of-service (DoS).
These include two high-severity privilege escalation vulnerabilities in Kernel components (CVE-2026-56914 and CVE-2026-58773), as well as 46 critical-severity vulnerabilities in various Pixel components, such as BigOcean, Bootloader, IP Multimedia Subsystem, and Trusted Execution Environment, that could lead to privilege escalation and remote code execution.
Security patch levels of 2026-09-05 or later resolve all the identified flaws. Users are advised to update their devices to the latest version by navigating to Settings > Security & privacy.
Back in June 2026, Google shipped patches for a high-severity flaw in Android’s Framework component (CVE-2025-48595, CVSS score: 8.4) that it said came under active exploitation.