Saltar al contenido
Jue. Oct 29th, 2026
Trending News: Attacker Tried to Exploit Alpine Linux’s GitLab via CVSS 10.0 Flaw Its Ruby Left OpenGitHub Launches npm Firewall to Block Malicious Packages Before InstallationLinux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other DistributionsFake ChatGPT and Claude Apps Abuse Signed Executables to Deploy Crypto Miners26,400 Valid Cloud and AI Credentials Found Exposed in Public Gitee RepositoriesGoogle’s Gemini 4 Carbon Leads Benchmarks for Finding, Exploiting, and Patching VulnerabilitiesHow AI Will Redefine Security Operations and CareersTelegram Android Flaw Lets Attackers Run Code When Users Answer Voice CallsCisco Patches Actively Exploited ASA and FTD VPN Flaw That Can Crash FirewallsHackers Exploited Cisco SD-WAN Flaw to Plant Malware Built to Steal Encryption KeysAttackers Exploit PHP2Shell Flaws in Internet-Exposed Palo Alto Networks Management InterfacesChina-Linked Hackers Exploited VMware ESX Zero-Day to Reduce Audit Trail VisibilityAdobe Commerce PolyShell Attacks Breach Hundreds of Stores as Brotli Exploit Traffic EmergesShinyHunters-Exploited Oracle PeopleSoft Zero-Day Turns Out to Be Three Chained FlawsResearcher Reveals How Logic Bugs Alone Cracked Microsoft Edge in $175,000 Pwn2Own WinVolt Typhoon Used Covert Silent Train Network in Four Zero-Day Exploitation CampaignsGoogle to Allow One-Tap Android App Installs From Approved Third-Party Stores Outside U.S.PHP2Shell Attack Roots 25 Servers, Breaches U.S. Government-Affiliated NetworkWazuh and AI for Enhanced SOC WorkflowsCritical 16-Year-Old UEFI Flaw Can Run Code Before Secure Boot on Network-Booting ServersHackers Target Critical Oracle E-Business Suite RCE Flaw Days After Security PatchSkyw4lker Device Code Phishing Campaign ExposedAdobe Fixes 8 Critical Campaign Classic Flaws Allowing Code Execution and Security BypassTailscale Patches SSH Flaws That Could Let Hacked Devices Gain Root Access on Other ServersFBI Seizes Virtualine Domain Over Alleged Criminal Hosting and Bitcoin Money LaunderingAnthropic’s Unreleased AI Model Chains Flaws Into Working Chrome, Safari, Windows and Linux ExploitsJapan’s GMO Offers $1 Million Bounty to Catch Hackers Behind FX Trading Cloud BreachCyberStrikeAI Uses 44 AI Agents to Automate Hacking Operations Against Japan TargetsApple Backports Fix for Exploited CoreGraphics Flaw to Older iPhones and iPadsGoAhead TLS Flaws Allow Revoked Client Certificates and Enable Session DecryptionLazarus Abuses South Korean Security Software to Deploy Malware Using Post-Quantum EncryptionAI-Generated Fake Login Pages Are Making Account Takeovers EasierKeystone to Destroy 18,835 Hardware Wallets After Hackers Steal Device Verification KeyMicrosoft Authenticator Flaw Let Permissionless Android Apps Steal Work Account TokensOpenAI Compaction Flaw Let Researchers Bypass Hidden Reasoning ProtectionsAustralia Gets Into Amadey Malware Backend, Cuts Off Access to 180,000 Infected ComputersAttackers Hijack Dahua IP Cameras in Ukraine Using P2P Access and Auth WeaknessesCISA Confirms Active Exploitation of Two PHP2Shell Flaws Enabling Remote Code ExecutionEl 35% de los ataques con infostealers comienza al ejecutar archivos descargadosEl grupo de extorsión MAJINAHANASHI ataca a Grupo Caliche y amenaza con filtrar DNIs y carnets de conducirUna operación de la policía ucraniana clausura un centenar de call centers fraudulentosEscudo Digital ya alertó de la brecha que ahora expone a los espías de MarruecosHackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on MagentoAttackers Use Microsoft Teams IT Support Scams to Deploy Malware and RansomwarePHP Issues Second Windows Security Update in Five Days to Fix Brotli Code Execution FlawThis2Shell, That2Shell, Everything’s an RCE? Rogue AI, Supply Chain Chaos and MoreTwo Critical Wasmtime Flaws Could Let Malicious WebAssembly Modules Escape SandboxesGheist Uses Stolen GitHub Tokens to Steal Private Repository Secrets via Actions LogsWhat Attackers Do in the Spaces Ordinary Detection MissesuCreator Android Spyware Can Steal Telegram 2FA Passwords and Clone WeChat AccountsMicrosoft 365 Token-Replay Attacks Compromise 97 Accounts at 79 OrganizationsMalicious File in Downloads Folder Tries to Trick AI Coding Agent Into Installing MalwarePHP2Shell Exploitation Hits Government Entity Amid Global Scanning and Signs of AI-Assisted HackingUnpatched Tailscale SSH Flaws Could Let a Hacked Device Reach Root on Other ServersOpenAI AI Agents Demonstrate VM Escapes and Secret Cross-Sandbox CommunicationGoogle Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted AdsLeaked LiteLLM Master Key Let Attackers Steal GitHub Tokens and Hijack Release PipelineBrotli Decoder Flaw Behind Node.js RCE Also Affects Bun, Python and Other Widely Used SoftwareResearchers Push Over 2 Million Updates to Remotely Disable Popcorn Time Updater That Could Fuel a BotnetCISA Flags Two Actively Exploited Critical Flaws in Collabora Online and Arista VeloCloudExposed Infrastructure Reveals How Ransomware Affiliates Used AI Agents to Execute IntrusionsBlackX UEFI Bootkit Bypasses Secure Boot on Patched Windows Systems Missing RevocationsRuby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE FlawsHackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 CredentialsPHP2Shell Exploit Attempts Hit Millions as Attackers Try to Deploy Mirai MalwareRussian-Linked Hackers Used New Mesh Network Backdoor in Destructive Ukraine AttackPHP Warns of Another Unpatched RCE Two Days After Emergency PHP2Shell PatchesCritical Flaw in Python’s Popular Pillow Image Library Allows Code Execution via a Crafted ImageCritical x402 SDK Flaw Could Let Malicious APIs Drain AI Agents’ Token BalancesResearchers Demonstrate Node2Shell RCE Exploit on Node.js Build Using Crafted Brotli DataTwo CVSS 9.0 Linux KSMBD RCE Flaws Disclosed on Public Mailing Lists Before Kernel FixesArista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in AttacksZelenski pone la ciberseguridad ucraniana en manos de su nuevo jefe de Seguridad y DefensaEl hacker de TuLotero pone a la venta los datos de los clientes, con cientos de miles de copias de DNIsLas cámaras IP se convierten en un nuevo vector de entrada para los ciberdelincuentesFalsos agentes de aerolíneas captan en redes a pasajeros para robarles datos por WhatsAppCondenan a cuatro años de cárcel a uno de los integrantes del peligroso grupo de ransomware ContiAI Secrets Leak, PingCAP Source Theft, Signal Hang-Up Flaw, Laravel Auth Bypass + 21 MoreeMudhra to Exit Global SSL/TLS Business After 8 Intermediate CA Keys Found Easily GuessableMeta Ordered to Pay $25 Billion After Court Finds 43 Million Privacy ViolationsSomeone Tried to Exploit PHP2Shell 4 Days Before the Vulnerabilities Were Publicly DisclosedWatch Expert Webinar On Your Newest Insider ThreatINTERPOL Arrests 1,462 Suspects, Disrupts 10,909 Cybercrime Networks in Global CrackdownOpenCode Flaw Lets Malicious MCP Servers Execute Code During Sign-In on Windows and WSLRailway Says Intruder May Have Accessed Customer Secrets, Urges Credential RotationNew QPACK Flaws Can Crash HTTP/3 Servers, Trigger Up to 4,000-Fold Memory AmplificationNode.js Brotli Decoder Bug Could Allow Remote Code Execution in All Supported VersionsLiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package ReleaseChina-Linked Hackers Use ARTEX AI Agents in ConnectWise Supply Chain AttackHackers Hid Vasilek Backdoor in VMware Tools During 2-Year Russian Healthcare IntrusionU.S. Orders DeepSeek Removed From Federal Civilian Systems, Bans New PurchasesCritical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of ReleasesUn grupo de hackers obtiene información sensible de empleados y clientes de BigMat en EspañaTres años de advertencias ignoradas: crónica del ciberataque a los supermercados francesesDécadas de secretos de Cartoon Network, expuestas en una filtración de datosLos cibercriminales utilizan ‘La Odisea’ como cebo para infectar ordenadoresReivindican el robo de más de 200 millones de filas de bases de datos de CanvaAttackers Hijacked Over 300 Tor Exit Relays to Intercept SSH ConnectionsLiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and BackdoorOpenAI’s GPT-6 Agent Removed Safety Monitoring, Then Falsely Denied Doing So
Chicago 12, Melborne City, USA
The Digital Fortress
  • Home
  • Blog
  • Sample Page
  • Get Started
Jue. Oct 29th, 2026
Trending News: Attacker Tried to Exploit Alpine Linux’s GitLab via CVSS 10.0 Flaw Its Ruby Left OpenGitHub Launches npm Firewall to Block Malicious Packages Before InstallationLinux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other DistributionsFake ChatGPT and Claude Apps Abuse Signed Executables to Deploy Crypto Miners26,400 Valid Cloud and AI Credentials Found Exposed in Public Gitee RepositoriesGoogle’s Gemini 4 Carbon Leads Benchmarks for Finding, Exploiting, and Patching VulnerabilitiesHow AI Will Redefine Security Operations and CareersTelegram Android Flaw Lets Attackers Run Code When Users Answer Voice CallsCisco Patches Actively Exploited ASA and FTD VPN Flaw That Can Crash FirewallsHackers Exploited Cisco SD-WAN Flaw to Plant Malware Built to Steal Encryption KeysAttackers Exploit PHP2Shell Flaws in Internet-Exposed Palo Alto Networks Management InterfacesChina-Linked Hackers Exploited VMware ESX Zero-Day to Reduce Audit Trail VisibilityAdobe Commerce PolyShell Attacks Breach Hundreds of Stores as Brotli Exploit Traffic EmergesShinyHunters-Exploited Oracle PeopleSoft Zero-Day Turns Out to Be Three Chained FlawsResearcher Reveals How Logic Bugs Alone Cracked Microsoft Edge in $175,000 Pwn2Own WinVolt Typhoon Used Covert Silent Train Network in Four Zero-Day Exploitation CampaignsGoogle to Allow One-Tap Android App Installs From Approved Third-Party Stores Outside U.S.PHP2Shell Attack Roots 25 Servers, Breaches U.S. Government-Affiliated NetworkWazuh and AI for Enhanced SOC WorkflowsCritical 16-Year-Old UEFI Flaw Can Run Code Before Secure Boot on Network-Booting ServersHackers Target Critical Oracle E-Business Suite RCE Flaw Days After Security PatchSkyw4lker Device Code Phishing Campaign ExposedAdobe Fixes 8 Critical Campaign Classic Flaws Allowing Code Execution and Security BypassTailscale Patches SSH Flaws That Could Let Hacked Devices Gain Root Access on Other ServersFBI Seizes Virtualine Domain Over Alleged Criminal Hosting and Bitcoin Money LaunderingAnthropic’s Unreleased AI Model Chains Flaws Into Working Chrome, Safari, Windows and Linux ExploitsJapan’s GMO Offers $1 Million Bounty to Catch Hackers Behind FX Trading Cloud BreachCyberStrikeAI Uses 44 AI Agents to Automate Hacking Operations Against Japan TargetsApple Backports Fix for Exploited CoreGraphics Flaw to Older iPhones and iPadsGoAhead TLS Flaws Allow Revoked Client Certificates and Enable Session DecryptionLazarus Abuses South Korean Security Software to Deploy Malware Using Post-Quantum EncryptionAI-Generated Fake Login Pages Are Making Account Takeovers EasierKeystone to Destroy 18,835 Hardware Wallets After Hackers Steal Device Verification KeyMicrosoft Authenticator Flaw Let Permissionless Android Apps Steal Work Account TokensOpenAI Compaction Flaw Let Researchers Bypass Hidden Reasoning ProtectionsAustralia Gets Into Amadey Malware Backend, Cuts Off Access to 180,000 Infected ComputersAttackers Hijack Dahua IP Cameras in Ukraine Using P2P Access and Auth WeaknessesCISA Confirms Active Exploitation of Two PHP2Shell Flaws Enabling Remote Code ExecutionEl 35% de los ataques con infostealers comienza al ejecutar archivos descargadosEl grupo de extorsión MAJINAHANASHI ataca a Grupo Caliche y amenaza con filtrar DNIs y carnets de conducirUna operación de la policía ucraniana clausura un centenar de call centers fraudulentosEscudo Digital ya alertó de la brecha que ahora expone a los espías de MarruecosHackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on MagentoAttackers Use Microsoft Teams IT Support Scams to Deploy Malware and RansomwarePHP Issues Second Windows Security Update in Five Days to Fix Brotli Code Execution FlawThis2Shell, That2Shell, Everything’s an RCE? Rogue AI, Supply Chain Chaos and MoreTwo Critical Wasmtime Flaws Could Let Malicious WebAssembly Modules Escape SandboxesGheist Uses Stolen GitHub Tokens to Steal Private Repository Secrets via Actions LogsWhat Attackers Do in the Spaces Ordinary Detection MissesuCreator Android Spyware Can Steal Telegram 2FA Passwords and Clone WeChat AccountsMicrosoft 365 Token-Replay Attacks Compromise 97 Accounts at 79 OrganizationsMalicious File in Downloads Folder Tries to Trick AI Coding Agent Into Installing MalwarePHP2Shell Exploitation Hits Government Entity Amid Global Scanning and Signs of AI-Assisted HackingUnpatched Tailscale SSH Flaws Could Let a Hacked Device Reach Root on Other ServersOpenAI AI Agents Demonstrate VM Escapes and Secret Cross-Sandbox CommunicationGoogle Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted AdsLeaked LiteLLM Master Key Let Attackers Steal GitHub Tokens and Hijack Release PipelineBrotli Decoder Flaw Behind Node.js RCE Also Affects Bun, Python and Other Widely Used SoftwareResearchers Push Over 2 Million Updates to Remotely Disable Popcorn Time Updater That Could Fuel a BotnetCISA Flags Two Actively Exploited Critical Flaws in Collabora Online and Arista VeloCloudExposed Infrastructure Reveals How Ransomware Affiliates Used AI Agents to Execute IntrusionsBlackX UEFI Bootkit Bypasses Secure Boot on Patched Windows Systems Missing RevocationsRuby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE FlawsHackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 CredentialsPHP2Shell Exploit Attempts Hit Millions as Attackers Try to Deploy Mirai MalwareRussian-Linked Hackers Used New Mesh Network Backdoor in Destructive Ukraine AttackPHP Warns of Another Unpatched RCE Two Days After Emergency PHP2Shell PatchesCritical Flaw in Python’s Popular Pillow Image Library Allows Code Execution via a Crafted ImageCritical x402 SDK Flaw Could Let Malicious APIs Drain AI Agents’ Token BalancesResearchers Demonstrate Node2Shell RCE Exploit on Node.js Build Using Crafted Brotli DataTwo CVSS 9.0 Linux KSMBD RCE Flaws Disclosed on Public Mailing Lists Before Kernel FixesArista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in AttacksZelenski pone la ciberseguridad ucraniana en manos de su nuevo jefe de Seguridad y DefensaEl hacker de TuLotero pone a la venta los datos de los clientes, con cientos de miles de copias de DNIsLas cámaras IP se convierten en un nuevo vector de entrada para los ciberdelincuentesFalsos agentes de aerolíneas captan en redes a pasajeros para robarles datos por WhatsAppCondenan a cuatro años de cárcel a uno de los integrantes del peligroso grupo de ransomware ContiAI Secrets Leak, PingCAP Source Theft, Signal Hang-Up Flaw, Laravel Auth Bypass + 21 MoreeMudhra to Exit Global SSL/TLS Business After 8 Intermediate CA Keys Found Easily GuessableMeta Ordered to Pay $25 Billion After Court Finds 43 Million Privacy ViolationsSomeone Tried to Exploit PHP2Shell 4 Days Before the Vulnerabilities Were Publicly DisclosedWatch Expert Webinar On Your Newest Insider ThreatINTERPOL Arrests 1,462 Suspects, Disrupts 10,909 Cybercrime Networks in Global CrackdownOpenCode Flaw Lets Malicious MCP Servers Execute Code During Sign-In on Windows and WSLRailway Says Intruder May Have Accessed Customer Secrets, Urges Credential RotationNew QPACK Flaws Can Crash HTTP/3 Servers, Trigger Up to 4,000-Fold Memory AmplificationNode.js Brotli Decoder Bug Could Allow Remote Code Execution in All Supported VersionsLiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package ReleaseChina-Linked Hackers Use ARTEX AI Agents in ConnectWise Supply Chain AttackHackers Hid Vasilek Backdoor in VMware Tools During 2-Year Russian Healthcare IntrusionU.S. Orders DeepSeek Removed From Federal Civilian Systems, Bans New PurchasesCritical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of ReleasesUn grupo de hackers obtiene información sensible de empleados y clientes de BigMat en EspañaTres años de advertencias ignoradas: crónica del ciberataque a los supermercados francesesDécadas de secretos de Cartoon Network, expuestas en una filtración de datosLos cibercriminales utilizan ‘La Odisea’ como cebo para infectar ordenadoresReivindican el robo de más de 200 millones de filas de bases de datos de CanvaAttackers Hijacked Over 300 Tor Exit Relays to Intercept SSH ConnectionsLiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and BackdoorOpenAI’s GPT-6 Agent Removed Safety Monitoring, Then Falsely Denied Doing So
Chicago 12, Melborne City, USA
  • Home
  • Blog
  • Sample Page
The Digital Fortress
  • Get Started

Archivos junio 2026

  1. Inicio
  2. 2026
  3. junio
RustDuck Botnet Rebuilds in Rust to Hijack Routers and Servers for DDoS
  • adminadmin
  • Botnet
  • DDoS
  • junio 30, 2026
  • 0 Comentarios
RustDuck Botnet Rebuilds in Rust to Hijack Routers and Servers for DDoS

A new two-stage malware family called RustDuck is hijacking home routers, IP cameras, Android boxes, and poorly secured servers, then stitching them into a network built to knock websites and…
Continue reading
Microsoft Warns Poisoned MCP Tool Descriptions Can Make AI Agents Leak Data
  • adminadmin
  • Agents
  • Data
  • junio 30, 2026
  • 0 Comentarios
Microsoft Warns Poisoned MCP Tool Descriptions Can Make AI Agents Leak Data

New Microsoft research shows how attackers can hijack AI agents that act on a user’s behalf, using nothing more than a poisoned tool description to make the agent quietly hand over company…

Continue reading
Langflow RCE Exploited to Deploy Monero Miner on Exposed AI App Endpoints
  • adminadmin
  • App
  • Deploy
  • junio 30, 2026
  • 0 Comentarios
Langflow RCE Exploited to Deploy Monero Miner on Exposed AI App Endpoints

Threat actors are continuing to exploit a critical Langflow vulnerability as part of fresh attacks designed to deliver a Monero cryptocurrency miner. The activity has been found to weaponize CVE-2026-33017…

Continue reading
Silent Swap Crypto Clipper Uses Fake Google Notes Extension to Replace Wallet Addresses
  • adminadmin
  • Addresses
  • Clipper
  • junio 30, 2026
  • 0 Comentarios
Silent Swap Crypto Clipper Uses Fake Google Notes Extension to Replace Wallet Addresses

Cybersecurity researchers have flagged an active browser extension campaign that is designed to steal cryptocurrency by stealthily replacing wallet addresses when unsuspecting users initiate a transaction. The cryptocurrency clipper activity…

Continue reading
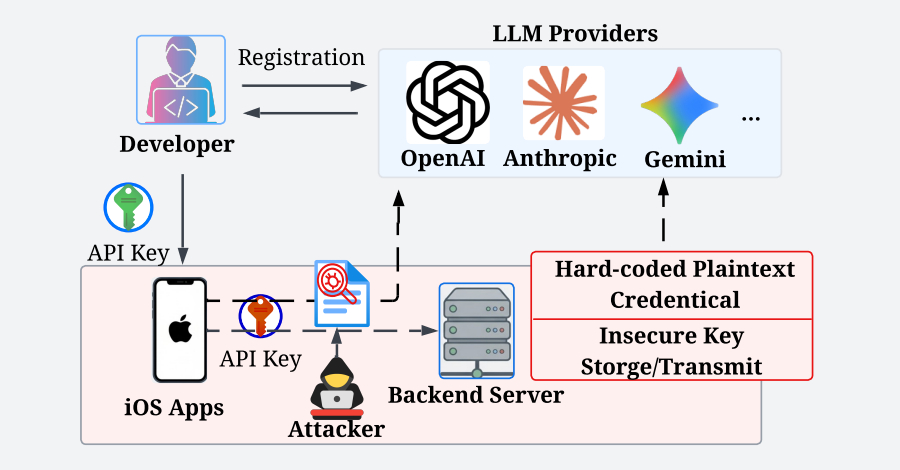
282 iOS AI Apps Leak API Keys and Open AI Proxy Access in Network Traffic Study
  • adminadmin
  • Access
  • API
  • junio 30, 2026
  • 0 Comentarios
282 iOS AI Apps Leak API Keys and Open AI Proxy Access in Network Traffic Study

Swati KhandelwalJun 30, 2026API Security / Mobile Security Researchers tested 444 AI chatbot apps for iPhone and found that 282 of them, nearly two-thirds, exposed paid AI access through their…

Continue reading
GuardFall Exposes Open-Source AI Coding Agents to Decades-Old Shell Injection Risks
  • adminadmin
  • Agents
  • Coding
  • junio 30, 2026
  • 0 Comentarios
GuardFall Exposes Open-Source AI Coding Agents to Decades-Old Shell Injection Risks

Swati KhandelwalJun 30, 2026AI Security / Software Supply Chain The safety check that is supposed to stop an AI coding agent from running a dangerous command can be walked straight…

Continue reading
What the Numbers Say About FIFA 2026 Cyber Risk
  • adminadmin
  • Cyber
  • FIFA
  • junio 30, 2026
  • 0 Comentarios
What the Numbers Say About FIFA 2026 Cyber Risk

The Hacker NewsJun 30, 2026Phishing / Impersonation The FIFA World Cup 2026 opened on June 11. By that date, according to Check Point Research, the fraud infrastructure targeting it had…

Continue reading
AirDrop and Quick Share Flaws Let Nearby Attackers Trigger Crashes and Bypass Checks
  • adminadmin
  • AirDrop
  • Attackers
  • junio 30, 2026
  • 0 Comentarios
AirDrop and Quick Share Flaws Let Nearby Attackers Trigger Crashes and Bypass Checks

Two researchers have found six security flaws in AirDrop and Quick Share, the wireless features that beam files between nearby devices with no cables or shared network. An attacker within…

Continue reading
Attackers Exploit SimpleHelp CVE-2026-48558 to Deploy TaskWeaver and Djinn Stealer
  • adminadmin
  • Attackers
  • CVE202648558
  • junio 30, 2026
  • 0 Comentarios
Attackers Exploit SimpleHelp CVE-2026-48558 to Deploy TaskWeaver and Djinn Stealer

An unknown threat actor has been observed exploiting a recently disclosed maximum-severity security flaw in SimpleHelp to deliver two previously unreported malware families, TaskWeaver and Djinn Stealer. The intrusion involves…

Continue reading
Progress Kemp LoadMaster Flaw Could Let Attackers Run Root Commands Pre-Auth
  • adminadmin
  • Attackers
  • Commands
  • junio 30, 2026
  • 0 Comentarios
Progress Kemp LoadMaster Flaw Could Let Attackers Run Root Commands Pre-Auth

Swati KhandelwalJun 30, 2026Vulnerability / API Security A critical vulnerability in Progress Kemp LoadMaster can let an unauthenticated attacker execute arbitrary commands as root on the appliance by sending a…

Continue reading

Paginación de entradas

1 2 … 21

Recent Posts

  • Attacker Tried to Exploit Alpine Linux’s GitLab via CVSS 10.0 Flaw Its Ruby Left Open
  • GitHub Launches npm Firewall to Block Malicious Packages Before Installation
  • Linux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other Distributions
  • Fake ChatGPT and Claude Apps Abuse Signed Executables to Deploy Crypto Miners
  • 26,400 Valid Cloud and AI Credentials Found Exposed in Public Gitee Repositories

Recent Comments

No hay comentarios que mostrar.

Archives

  • octubre 2026
  • septiembre 2026
  • agosto 2026
  • julio 2026
  • junio 2026
  • mayo 2026
  • abril 2026
  • marzo 2026
  • febrero 2026
  • agosto 2024

Categories

  • Uncategorized

Other Story

Uncategorized

Attacker Tried to Exploit Alpine Linux’s GitLab via CVSS 10.0 Flaw Its Ruby Left Open

  • admin
  • octubre 29, 2026
Attacker Tried to Exploit Alpine Linux’s GitLab via CVSS 10.0 Flaw Its Ruby Left Open
Uncategorized

GitHub Launches npm Firewall to Block Malicious Packages Before Installation

  • admin
  • octubre 29, 2026
GitHub Launches npm Firewall to Block Malicious Packages Before Installation
Uncategorized

Linux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other Distributions

  • admin
  • octubre 29, 2026
Linux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other Distributions
Uncategorized

Fake ChatGPT and Claude Apps Abuse Signed Executables to Deploy Crypto Miners

  • admin
  • octubre 29, 2026
Fake ChatGPT and Claude Apps Abuse Signed Executables to Deploy Crypto Miners
Uncategorized

26,400 Valid Cloud and AI Credentials Found Exposed in Public Gitee Repositories

  • admin
  • octubre 29, 2026
26,400 Valid Cloud and AI Credentials Found Exposed in Public Gitee Repositories
Uncategorized

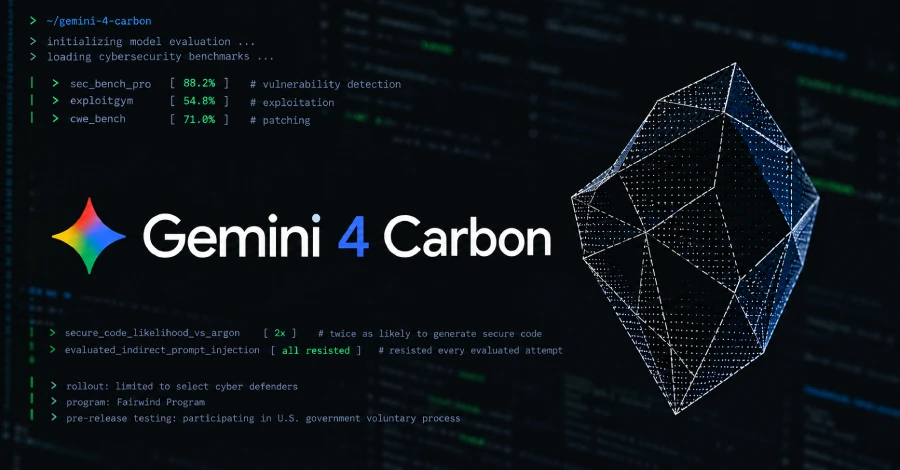
Google’s Gemini 4 Carbon Leads Benchmarks for Finding, Exploiting, and Patching Vulnerabilities

  • admin
  • octubre 29, 2026
Google’s Gemini 4 Carbon Leads Benchmarks for Finding, Exploiting, and Patching Vulnerabilities
Copyright © 2026 The Digital Fortress | Powered by Desert Themes
Back to Top