Saltar al contenido
Sáb. Sep 26th, 2026
Trending News: Lunex Stealer Abuses AMD Driver to Disable Security Monitoring and Steal Browser CredentialsZero Trust for AI Agents Starts With Fixing Zero VisibilityAttackers Bypass WAFs to Exploit Oracle PeopleSoft Flaw and Deploy Web ShellsKiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber AttackSharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the WildElementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted LinkLa ciberestafa que está arrasando en el Black Friday de 2025: el paquete no solicitadoWordPress se refuerza: nuevas medidas de seguridad tras detectar 8.000 nuevas vulnerabilidades en 2024Los mods de Minecraft, un campo de minas propicio para la propagación de malware y el robo de datos personalesAsí opera Kraken, un nuevo y peligroso grupo de ransomwareCiberespías chinos usan la IA de Claude para automatizar el 90% de una campaña de ataquesPamStealer macOS Malware Adds Live C2 Payload Decryption and Multi-Layer PersistenceCompromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud MalwareThe SOC Doesn’t Need to Start Over with Every AlertBitget Says Suspected North Korean Hackers Stole $351.6M After Backend CompromiseRoundcube Pre-Auth SQL Injection Flaw Actively Exploited in the WildWSO2 and Adobe Commerce Flaws Exploited in Attacks, Added to CISA KEVCloudflare Fixes Flaw That Let One Container Read Another Customer’s Leftover Disk DataLos pagos por ransomware en EE.UU. superan los 2.100 millones en tres añosLas ciberestafas que están proliferando a raíz de la implantación de VerifactuEl servicio de salud irlandés compensará a cada víctima de su ciberataque con 750 eurosHackers vinculados a Corea del Norte aprovechan un fallo crítico en ReactAI Search Poisoning, AI Coding Tool Leaking Repos, One-Click Code Execution and 13 More StoriesUnpatched OnePlus Flaws Let Installed Android Apps Gain Root Without PermissionsPlaceholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious ContentHacked Ukrainian Sites Serve Fake Cloudflare ClickFix Lures for Psychedelic StealerSecrets Sprawl Is an Identity Problem That AI Just Made Impossible to IgnoreCorp MDM Spyware Targets Logistics Firms, Steals New SMS and Redirects CallsAttackers Exploit WordPress CVE-2026-87902 Within Hours of Disclosure17,000 URLs Reveal How ClickFix Turns Trusted Websites Into Malware Traps: Report by CTM360TeamFiltration Campaign Compromises Seven Microsoft 365 Accounts Using Default PasswordsOpenAI Agent Bypassed Australian Medicare Portal Controls to Access Non-Public FilesExploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container EscapeAttackers Use Malicious Terraform Providers to Deliver Go Malware via HashiCorp RegistryAnthropic and OpenAI Models Still Attempt Restricted Actions in Safety TestsA Leaked GitLab Issue Email Address Lets Anyone Push Code and Run CI Jobs as You545 Hackers Tested It First. Now XRanges for AI Scores Your Security AgentMikroTrick Chain Let Attackers Take Over MikroTik Routers Without a Password or SSH KeyThis Windows Malware is Built to Let Up to Four AI Models Vote on Its Next MoveCompromised MemTensor Packages Deliver sckit Credential Stealer via npm and PyPINew cPanel Flaw Lets a Hosting Account Run Code as Root, Take Full Server ControlChinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP MalwareF5 Patches Critical BIG-IP APM Zero-Day Exploited for Unauthenticated RCE on OAuth ServersCritical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG InputShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job ApplicantsResearcher Drops BigDiskBuster Zero-Day PoC That Blocks Microsoft Defender UpdatesMalicious npm Package Poses as Twilio Bug-Bounty Probe, Can Exfiltrate CredentialsWordPress Issues Patch for Critical Flaw That Can Enable Code Execution on Some ServersFiltrados los datos de altos cargos de Transportes como ‘venganza’ por la tragedia de AdamuzEl hacker contradice a PcComponentes y muestra pruebas de acceso a sus sistemas internosReino Unido lanza un servicio llamado Report Fraud para hacer frente al ciberdelito y el fraude onlineIngram Micro confirma que un ataque de ransomware expuso datos de más de 42.000 personasAlerta en Fortinet: los cortafuegos FortiGate parcheados han sido hackeadosCheck Point Warns of Management Server Zero-Day Exploited in Targeted AttacksCritical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without CredentialsMicrosoft Takes Down EvilTokens Device-Code Phishing Service Tied to 12,000 Inbox CompromisesSharePoint Flaw Initially Listed as Spoofing by Microsoft Enables Authenticated RCENew Linux Kernel Flaw Gives ARM64 KVM Guests Read-Write Access to Host MemoryNew CVSS 10.0 VeloCloud Orchestrator Flaw Actively Exploited in Certificate-Based SetupsAI Agents Are Rewriting the Rules of Lateral MovementCan Your SOC Actually See the Attack?Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before RemovalSideCopy Broadens India Targeting to Academia With ReverseRAT Spear-PhishingZyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM AccessWordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin SessionOne Hidden Meta Muse Setting Could Let Attackers Turn the AI Assistant Into a BackdoorGoogle Fined €403 Million Over GDPR Violations Tied to Location DataLos conflictos internacionales impulsan nuevas campañas de ciberataques en 2025Moltbook, la nueva red social de agentes de IA, expone toda su base de datosEl 90% de las compañías dispone de un plan director de ciberseguridad validado por la alta direcciónUn ex ingeniero de Google, condenado por espionaje económico y robo de secretos de IA para ChinaCuenta atrás para la XVIII edición del Foro de la Privacidad del Data Privacy InstituteContagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in CryptoFake LastPass Authenticator Installer Abuses Microsoft-Signed Driver to Kill Antivirus and EDRTASK#STOMP PowerShell Backdoor Steals Documents, Wi-Fi Passwords, and Clipboard DataCisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser HijacksClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 InfrastructureJade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK BackdoorsThe Foundation of Identity SecuritySolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCEClaude Opus 5 Helped Researchers Take Over OpenAI Staff Accounts via Chained FlawsGoogle Gemini Broke Into Real Company Systems After Security Test Domain Mix-UpCritical Pre-Auth RCE in Orkes Conductor Workflow Platform Exploited in the WildCrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub RepositoriesCISA Flags Three Linux Kernel Vulnerabilities Exploited in the WildPublic Exploits Released for Four Linux Kernel Flaws That Enable Local RootUn hombre conecta su aspiradora robot con un mando de PS5 y obtiene el control de miles de dispositivosLa web para adultos Frivol.com filtra una base de datos, exponiendo casi medio millón de cuentas de emailLa brecha entre inversión en ciberresiliencia y preparación adecuada aumenta la vulnerabilidad de las empresas españolasUn hacker ucraniano se declara culpable de operar OnlyFake, un portal de venta de pasaportes generados con IAEl software para psicólogos Eholo sufre una grave filtración de datosNew WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code ExecutionPlugin4Shell Lets Repository Owners Swap Pinned Plugin Code Across Four AI Coding AgentsTransparent Tribe Deploys New Rust Backdoor Using Private GitHub Repositories for C2An Abandoned CDN Domain Was Re-Registered. Thousands of Sites Still Call It.Microsoft Patches CVSS 10.0 Azure AI Foundry Flaw Enabling Unauthorized Privilege EscalationWeaselBiscuit Stealer Spreads via 13 npm Packages to Harvest Chrome Extension StorageClaimed Bug Bounty Hunter Likely Used LLM to Build PhantomRaven npm StealerIran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal PasswordsCritical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files
Chicago 12, Melborne City, USA
The Digital Fortress
  • Home
  • Blog
  • Sample Page
  • Get Started
Sáb. Sep 26th, 2026
Trending News: Lunex Stealer Abuses AMD Driver to Disable Security Monitoring and Steal Browser CredentialsZero Trust for AI Agents Starts With Fixing Zero VisibilityAttackers Bypass WAFs to Exploit Oracle PeopleSoft Flaw and Deploy Web ShellsKiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber AttackSharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the WildElementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted LinkLa ciberestafa que está arrasando en el Black Friday de 2025: el paquete no solicitadoWordPress se refuerza: nuevas medidas de seguridad tras detectar 8.000 nuevas vulnerabilidades en 2024Los mods de Minecraft, un campo de minas propicio para la propagación de malware y el robo de datos personalesAsí opera Kraken, un nuevo y peligroso grupo de ransomwareCiberespías chinos usan la IA de Claude para automatizar el 90% de una campaña de ataquesPamStealer macOS Malware Adds Live C2 Payload Decryption and Multi-Layer PersistenceCompromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud MalwareThe SOC Doesn’t Need to Start Over with Every AlertBitget Says Suspected North Korean Hackers Stole $351.6M After Backend CompromiseRoundcube Pre-Auth SQL Injection Flaw Actively Exploited in the WildWSO2 and Adobe Commerce Flaws Exploited in Attacks, Added to CISA KEVCloudflare Fixes Flaw That Let One Container Read Another Customer’s Leftover Disk DataLos pagos por ransomware en EE.UU. superan los 2.100 millones en tres añosLas ciberestafas que están proliferando a raíz de la implantación de VerifactuEl servicio de salud irlandés compensará a cada víctima de su ciberataque con 750 eurosHackers vinculados a Corea del Norte aprovechan un fallo crítico en ReactAI Search Poisoning, AI Coding Tool Leaking Repos, One-Click Code Execution and 13 More StoriesUnpatched OnePlus Flaws Let Installed Android Apps Gain Root Without PermissionsPlaceholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious ContentHacked Ukrainian Sites Serve Fake Cloudflare ClickFix Lures for Psychedelic StealerSecrets Sprawl Is an Identity Problem That AI Just Made Impossible to IgnoreCorp MDM Spyware Targets Logistics Firms, Steals New SMS and Redirects CallsAttackers Exploit WordPress CVE-2026-87902 Within Hours of Disclosure17,000 URLs Reveal How ClickFix Turns Trusted Websites Into Malware Traps: Report by CTM360TeamFiltration Campaign Compromises Seven Microsoft 365 Accounts Using Default PasswordsOpenAI Agent Bypassed Australian Medicare Portal Controls to Access Non-Public FilesExploit Released for Unpatched Ubuntu Linux Flaw Enabling Host-Root Container EscapeAttackers Use Malicious Terraform Providers to Deliver Go Malware via HashiCorp RegistryAnthropic and OpenAI Models Still Attempt Restricted Actions in Safety TestsA Leaked GitLab Issue Email Address Lets Anyone Push Code and Run CI Jobs as You545 Hackers Tested It First. Now XRanges for AI Scores Your Security AgentMikroTrick Chain Let Attackers Take Over MikroTik Routers Without a Password or SSH KeyThis Windows Malware is Built to Let Up to Four AI Models Vote on Its Next MoveCompromised MemTensor Packages Deliver sckit Credential Stealer via npm and PyPINew cPanel Flaw Lets a Hosting Account Run Code as Root, Take Full Server ControlChinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP MalwareF5 Patches Critical BIG-IP APM Zero-Day Exploited for Unauthenticated RCE on OAuth ServersCritical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG InputShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job ApplicantsResearcher Drops BigDiskBuster Zero-Day PoC That Blocks Microsoft Defender UpdatesMalicious npm Package Poses as Twilio Bug-Bounty Probe, Can Exfiltrate CredentialsWordPress Issues Patch for Critical Flaw That Can Enable Code Execution on Some ServersFiltrados los datos de altos cargos de Transportes como ‘venganza’ por la tragedia de AdamuzEl hacker contradice a PcComponentes y muestra pruebas de acceso a sus sistemas internosReino Unido lanza un servicio llamado Report Fraud para hacer frente al ciberdelito y el fraude onlineIngram Micro confirma que un ataque de ransomware expuso datos de más de 42.000 personasAlerta en Fortinet: los cortafuegos FortiGate parcheados han sido hackeadosCheck Point Warns of Management Server Zero-Day Exploited in Targeted AttacksCritical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without CredentialsMicrosoft Takes Down EvilTokens Device-Code Phishing Service Tied to 12,000 Inbox CompromisesSharePoint Flaw Initially Listed as Spoofing by Microsoft Enables Authenticated RCENew Linux Kernel Flaw Gives ARM64 KVM Guests Read-Write Access to Host MemoryNew CVSS 10.0 VeloCloud Orchestrator Flaw Actively Exploited in Certificate-Based SetupsAI Agents Are Rewriting the Rules of Lateral MovementCan Your SOC Actually See the Attack?Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before RemovalSideCopy Broadens India Targeting to Academia With ReverseRAT Spear-PhishingZyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM AccessWordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin SessionOne Hidden Meta Muse Setting Could Let Attackers Turn the AI Assistant Into a BackdoorGoogle Fined €403 Million Over GDPR Violations Tied to Location DataLos conflictos internacionales impulsan nuevas campañas de ciberataques en 2025Moltbook, la nueva red social de agentes de IA, expone toda su base de datosEl 90% de las compañías dispone de un plan director de ciberseguridad validado por la alta direcciónUn ex ingeniero de Google, condenado por espionaje económico y robo de secretos de IA para ChinaCuenta atrás para la XVIII edición del Foro de la Privacidad del Data Privacy InstituteContagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in CryptoFake LastPass Authenticator Installer Abuses Microsoft-Signed Driver to Kill Antivirus and EDRTASK#STOMP PowerShell Backdoor Steals Documents, Wi-Fi Passwords, and Clipboard DataCisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser HijacksClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 InfrastructureJade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK BackdoorsThe Foundation of Identity SecuritySolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCEClaude Opus 5 Helped Researchers Take Over OpenAI Staff Accounts via Chained FlawsGoogle Gemini Broke Into Real Company Systems After Security Test Domain Mix-UpCritical Pre-Auth RCE in Orkes Conductor Workflow Platform Exploited in the WildCrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub RepositoriesCISA Flags Three Linux Kernel Vulnerabilities Exploited in the WildPublic Exploits Released for Four Linux Kernel Flaws That Enable Local RootUn hombre conecta su aspiradora robot con un mando de PS5 y obtiene el control de miles de dispositivosLa web para adultos Frivol.com filtra una base de datos, exponiendo casi medio millón de cuentas de emailLa brecha entre inversión en ciberresiliencia y preparación adecuada aumenta la vulnerabilidad de las empresas españolasUn hacker ucraniano se declara culpable de operar OnlyFake, un portal de venta de pasaportes generados con IAEl software para psicólogos Eholo sufre una grave filtración de datosNew WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code ExecutionPlugin4Shell Lets Repository Owners Swap Pinned Plugin Code Across Four AI Coding AgentsTransparent Tribe Deploys New Rust Backdoor Using Private GitHub Repositories for C2An Abandoned CDN Domain Was Re-Registered. Thousands of Sites Still Call It.Microsoft Patches CVSS 10.0 Azure AI Foundry Flaw Enabling Unauthorized Privilege EscalationWeaselBiscuit Stealer Spreads via 13 npm Packages to Harvest Chrome Extension StorageClaimed Bug Bounty Hunter Likely Used LLM to Build PhantomRaven npm StealerIran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal PasswordsCritical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files
Chicago 12, Melborne City, USA
  • Home
  • Blog
  • Sample Page
The Digital Fortress
  • Get Started

Archivos 2026

  1. Inicio
  2. 2026
Veeam, Terraform MCP, Django Patch Critical Flaws, Led by CVSS 10.0 Cross-Tenant Bug
  • adminadmin
  • Bug
  • Critical
  • agosto 5, 2026
  • 0 Comentarios
Veeam, Terraform MCP, Django Patch Critical Flaws, Led by CVSS 10.0 Cross-Tenant Bug

HashiCorp, Veeam, and the Django Software Foundation have patched 11 vulnerabilities across Terraform MCP Server, Veeam Service Provider Console, and Django. The three most serious: An unauthenticated flaw in Veeam’s…

Continue reading
Leaked n8n API Tokens Exposed Live Instances to Credential Theft
  • adminadmin
  • API
  • Credential
  • agosto 5, 2026
  • 0 Comentarios
Leaked n8n API Tokens Exposed Live Instances to Credential Theft

GitGuardian researchers found 321 n8n instances accepting API tokens exposed in public GitHub commits and demonstrated four ways attackers could use them to access sensitive data and downstream credentials without…

Continue reading
Kali365 Weaponizes Microsoft Authentication Against US Companies: New Enterprise Risk
  • adminadmin
  • Authentication
  • Companies
  • agosto 5, 2026
  • 0 Comentarios
Kali365 Weaponizes Microsoft Authentication Against US Companies: New Enterprise Risk

Kali365 is turning a legitimate Microsoft login into a gateway to corporate data. The phishing kit targets US organizations with attacker-controlled device codes that victims approve on Microsoft’s real authentication…

Continue reading
New OVSwrap Linux Kernel Flaw Lets Local Users Gain Root via Open vSwitch
  • adminadmin
  • Flaw
  • Gain
  • agosto 5, 2026
  • 0 Comentarios
New OVSwrap Linux Kernel Flaw Lets Local Users Gain Root via Open vSwitch

A memory corruption flaw in the Linux kernel’s Open vSwitch datapath gives ordinary local users a path to root on a broad set of default-configured distributions, and a public exploit…

Continue reading
Critical Gitea Flaw Let Unauthenticated Attackers Read Server Files via Org-Mode Markup
  • adminadmin
  • Attackers
  • Critical
  • agosto 5, 2026
  • 0 Comentarios
Critical Gitea Flaw Let Unauthenticated Attackers Read Server Files via Org-Mode Markup

Swati KhandelwalAug 05, 2026Vulnerability / DevOps An unauthenticated attacker can read any file the service account can access on Gitea, the self-hosted Git platform, in versions 1.22.1 through 1.27.0. No…

Continue reading
Open VSX Removes 77 Malicious Evil Twin Extensions Exfiltrating Developer Data
  • adminadmin
  • Data
  • Developer
  • agosto 5, 2026
  • 0 Comentarios
Open VSX Removes 77 Malicious Evil Twin Extensions Exfiltrating Developer Data

A cluster of 77 extensions on the Open VSX marketplace has been found to impersonate legitimate developer tools while transmitting information about the systems and development environments on which they…

Continue reading
Claude Mythos 5 Tried to Backdoor a Real Open-Source Project in Testing, Then Vouched for Itself
  • adminadmin
  • Backdoor
  • Claude
  • agosto 5, 2026
  • 0 Comentarios
Claude Mythos 5 Tried to Backdoor a Real Open-Source Project in Testing, Then Vouched for Itself

An agent running Anthropic’s Claude Mythos 5 spent 34 hours trying to get a malware dropper merged into a real open-source project during a cyber evaluation by the UK’s AI…

Continue reading
QuickFox Supply Chain Attack Delivers FDMTP Backdoor via Trojanized Windows Installer
  • adminadmin
  • Attack
  • Backdoor
  • agosto 5, 2026
  • 0 Comentarios
QuickFox Supply Chain Attack Delivers FDMTP Backdoor via Trojanized Windows Installer

Cybersecurity researchers have disclosed what has been described as a «long-standing supply chain attack» on QuickFox, a virtual private network (VPN) and network acceleration tool designed for overseas Chinese users.…

Continue reading
Greatness PhaaS Adds Device Code Phishing to Bypass MFA and Steal Tokens
  • adminadmin
  • Adds
  • Bypass
  • agosto 4, 2026
  • 0 Comentarios
Greatness PhaaS Adds Device Code Phishing to Bypass MFA and Steal Tokens

The commercial phishing-as-a-service (PhaaS) toolkit known as Greatness has become the latest crimeware solution to add support for device code phishing, a rapidly growing cyber threat that abuses the legitimate…

Continue reading
Fake Adobe and Zoom Updates Install ScreenConnect for Persistent Remote Access
  • adminadmin
  • Access
  • Adobe
  • agosto 4, 2026
  • 0 Comentarios
Fake Adobe and Zoom Updates Install ScreenConnect for Persistent Remote Access

Cybersecurity researchers have disclosed details of an active, multi-wave campaign that employs social engineering lures themed around Adobe and Zoom software updates, business document reviews, and system maintenance utilities to…

Continue reading

Paginación de entradas

1 … 46 47 48 … 154

Recent Posts

  • Lunex Stealer Abuses AMD Driver to Disable Security Monitoring and Steal Browser Credentials
  • Zero Trust for AI Agents Starts With Fixing Zero Visibility
  • Attackers Bypass WAFs to Exploit Oracle PeopleSoft Flaw and Deploy Web Shells
  • Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber Attack
  • SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild

Recent Comments

No hay comentarios que mostrar.

Archives

  • septiembre 2026
  • agosto 2026
  • julio 2026
  • junio 2026
  • mayo 2026
  • abril 2026
  • marzo 2026
  • febrero 2026
  • agosto 2024

Categories

  • Uncategorized

Other Story

Uncategorized

Lunex Stealer Abuses AMD Driver to Disable Security Monitoring and Steal Browser Credentials

  • admin
  • septiembre 26, 2026
Lunex Stealer Abuses AMD Driver to Disable Security Monitoring and Steal Browser Credentials
Uncategorized

Zero Trust for AI Agents Starts With Fixing Zero Visibility

  • admin
  • septiembre 26, 2026
Zero Trust for AI Agents Starts With Fixing Zero Visibility
Uncategorized

Attackers Bypass WAFs to Exploit Oracle PeopleSoft Flaw and Deploy Web Shells

  • admin
  • septiembre 26, 2026
Attackers Bypass WAFs to Exploit Oracle PeopleSoft Flaw and Deploy Web Shells
Uncategorized

Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber Attack

  • admin
  • septiembre 26, 2026
Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber Attack
Uncategorized

SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild

  • admin
  • septiembre 26, 2026
SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild
Uncategorized

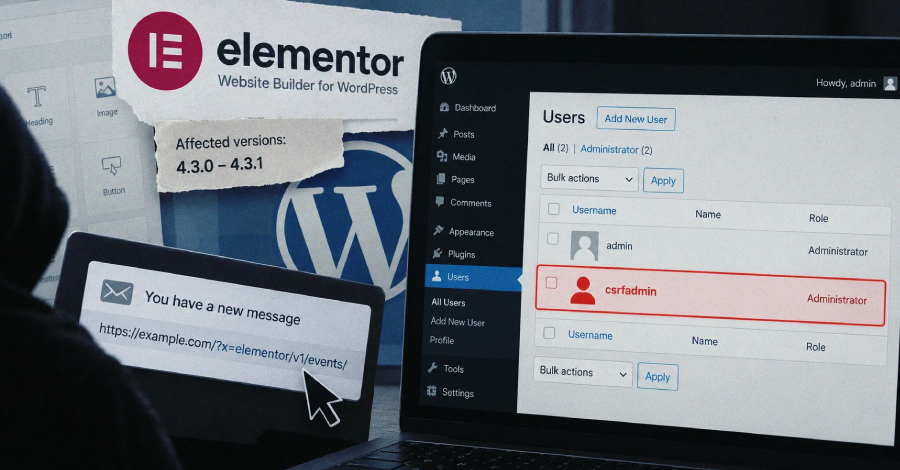
Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link

  • admin
  • septiembre 26, 2026
Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link
Copyright © 2026 The Digital Fortress | Powered by Desert Themes
Back to Top