Saltar al contenido
Vie. Sep 18th, 2026
Trending News: U.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS AttacksCisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active AttacksGyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata RecordsUn ciberataque contra Inditex afecta a sus bases de datos internasHackean a una empresa de ciberseguridad y exponen datos y cámaras de clientesLos datos de los funcionarios del Palacio Real de Marruecos, en manos de un hacker75.000 sospechosos identificados y decenas de infraestructuras DDoS desmanteladas tras un macrooperativo internacionalEl organismo oficial de EE.UU. que clasifica las vulnerabilidades de ciberseguridad no da a bastoBIND 9 Update Fixes 14 Flaws, Including an Unauthenticated Crash Over DNS-over-HTTPSOpenAI Reveals Six Model Incidents Involving Hidden Failures and Unauthorized UploadsChina-Aligned FamousSparrow Deploys SparroWocky Backdoor Across Latin AmericaCISO’s Expert Guide to Agentic Pentesting for WebsitesCan You Prove a New CVE Is Exploitable Before Attackers Do? Learn How in This WebinarCritical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS ZoneAcronis cPanel Backup Plugin Vulnerability Exploited in Targeted AttacksC1b3rwall se arma contra la crisis de ciberseguridad que amenaza la supervivencia de las empresas españolasCarnival promete relax y lujo en sus cruceros; los hackers encontraron además millones de perfiles personalesUn hacker canadiense de 23 años, detenido por operar la botnet KimwolfUn gigante de la logística sufre una brecha de datos de 840 millones de registrosLos ciberdelincuentes ya no respetan ni los carros de la compraThreat Intelligence Alone Won’t Close the Exploitation GapOne Extension Could Hijack AI Assistants Across Chrome, Comet, Edge, Opera Neon and ClaudeThree Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and WipersAttackers Exploit Issabel Framework Flaw Enabling Unauthenticated OS Command ExecutionParallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can’t Install FixAttacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 RepositoriesA New Challenge for Identity SecurityGoogle Patches Pixel Modem Flaw Amid Signs of Limited Targeted ExploitationActive Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin TokensAttackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web ShellsSi pierdes el móvil este verano, haz esto en los primeros cinco minutos para que no vacíen tus cuentasHalluSquatting, el nuevo truco para engañar a los asistentes de IA y colar malware en tu ordenadorUn hacker adolescente piratea el servicio de streaming de Bandai usando ChatGPTUna agencia de EE.UU. pagó un millón de dólares tras casi un mes de negociación con un grupo de ransomwareUn ciberataque deja sin suministro a KFC y obliga a cerrar temporalmente algunos restaurantesKREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session TokensIranian Hackers Use Telegram-Controlled Malware to Spy on Dissidents and JournalistsBambooToken Malware Uses MQTT to Control Windows and Linux SystemsMass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev ServersWhy Testing Individual Techniques Misses the PointHuman Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight SecondsLiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared ServerChina-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGECisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command ExecutionWordPress Adds Automated Plugin Reviews to Block High-Risk Updates Before DistributionTelegram Desktop Flaw Lets Hidden JavaScript Exfiltrate Messages From HTML ExportsPaperCut alerta de ataques activos contra sus programas de gestión de impresorasLas Fuerzas Armadas y la Guardia Civil aceleran su transformación digital ante un ciberespacio cada vez más complejoCuidado con estos anuncios de Facebook: parecen de Google Play, pero conducen a casinos sin licenciaUna filtración revela cómo Rusia ha creado una cantera universitaria para sus ciberoperaciones militaresUn fallo en Lenovo ID permite el acceso sin autorización a unas 5.000 cuentas de Dropbox3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber CredentialsRed Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six CountriesNew DDRop Attack Breaks Intel TDX and AMD SEV-SNP Confidential ComputingRogue AI Agents, WeChat Worm, PaperCut Attacks, AI Espionage, and RootkitsAI Changed the Exposure Problem. Validation Needs to Change With It.Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 UsersAttackers Use Passkey Phishing to Hijack Microsoft Cloud Accounts and Exfiltrate DataCISA Adds 5 Actively Exploited Artifactory, ScreenConnect, and RouterOS Flaws to KEVWhat It Does to Your SOCOpenAI Agents Linked to RubyGems Campaign That Gained RCE on RubyDoc ServersAnthropic Says Seven China-Based AI Labs Ran Industrial-Scale Claude Distillation AttacksGitLab CVSS 10 File-Read Flaw Draws In-the-Wild Probes After DisclosureRussian State-Sponsored Hackers Use Claude to Rebuild Malware After DetectionClaude Used to Automate Exploitation and Data Theft Across Multiple VictimsYour Critical Vulnerabilities Might Not Be Your Biggest RiskCisco FMC Flaws Exploited to Steal Credentials and Deploy Qilin RansomwarePaperCut Replaces Emergency Patches With Fixes for Two Actively Exploited FlawsChina-Linked UNC3569 Exploited Sogou Input Method Flaw to Deploy GRAYRABBIT BackdoorAttackers Chain JFrog Artifactory Flaws to Gain Admin Control and Plant Backdoors200 Android Flaws, Browser-Built Phishing, 119K Scam Shops + 23 More StoriesGigabud Creates Android Work Profiles to Hide From Banking App Malware ChecksGoogle Play Early Access Abused to Push Thousands of Deceptive Android AppsPaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ InstancesCheck Point Discloses Two 9.8-Rated VPN Certificate Flaws Enabling Unauthenticated RCECISA Flags Exploited Cisco, Citrix, Fortinet Flaws, Sets Sept. 12 Federal Patch DeadlineAnthropic Discloses Fourth AI Hacking Incident Involving Claude Opus 4.6Nearly 1 in 10 Exposed LiteLLM Gateways Accepted the Example «sk-1234» Admin KeyFour Spy Groups Used the Same Chrome and Windows Exploit Kit Within a WeekU.S. Disrupts Xinbi Guarantee Scam Marketplace, Freezes $52.8 Million in CryptoSAP Patches CVSS 10.0 Kernel Flaw Enabling Unauthenticated Remote Code ExecutionResearcher Drops New Microsoft Defender PoC Showing ShieldBreak Patch Can Be BypassedF5 BIG-IP APM Malware Injects a PHP Web Shell Into Memory, Evading Disk ScansU.S. Agencies Accuse China AI Firms of Distilling Claude, GPT, Gemini, and GrokInfostealer Logs Expose Replayable AI Tokens That Can Bypass MFALearn How to Answer “Are We Exposed?” Faster After a New CVEAlby Hub Critical Flaw Could Let Attackers Take Over Internet-Exposed Bitcoin WalletsDeepSeek Harness Flaw Let AI Agents Disable Their Own File Sandbox Without ApprovalNew cPanel Flaw Lets a Hosting Account With Mail Privileges Run Code as RootChrome V8 Zero-Day Exploited in the Wild Enables Code Execution Inside SandboxMicrosoft Patches Record 974 Flaws, Including Two Exploited Windows Zero-DaysN-able N-central Pre-Auth RCE Flaw Exploited in the WildAutonomous AI Agents Compromise Thousands of Credentials in Under Six HoursChatGPT Flaw Let a Planted Prompt Send a Victim’s Gmail Data to Another AccountSlim Spider Steals Crypto Custody Secrets From Brazilian Financial InstitutionLiquid Hackers Return 3,400 Bitcoin Taken via Elements Bug, Still Holding $47M in BTCWhat It Took to Reach 1 Billion Build ManifestsWeChat Zero-Click Worm Took Over Accounts on iPhone and Android via Incoming CallsBengalSEO Poisons Bing Search Results to Deliver MayaBot and Tech Support ScamsFreeIPA Flaw Chain Lets Anonymous Clients Create Reusable Administrator Credentials
Chicago 12, Melborne City, USA
The Digital Fortress
  • Home
  • Blog
  • Sample Page
  • Get Started
Vie. Sep 18th, 2026
Trending News: U.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS AttacksCisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active AttacksGyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata RecordsUn ciberataque contra Inditex afecta a sus bases de datos internasHackean a una empresa de ciberseguridad y exponen datos y cámaras de clientesLos datos de los funcionarios del Palacio Real de Marruecos, en manos de un hacker75.000 sospechosos identificados y decenas de infraestructuras DDoS desmanteladas tras un macrooperativo internacionalEl organismo oficial de EE.UU. que clasifica las vulnerabilidades de ciberseguridad no da a bastoBIND 9 Update Fixes 14 Flaws, Including an Unauthenticated Crash Over DNS-over-HTTPSOpenAI Reveals Six Model Incidents Involving Hidden Failures and Unauthorized UploadsChina-Aligned FamousSparrow Deploys SparroWocky Backdoor Across Latin AmericaCISO’s Expert Guide to Agentic Pentesting for WebsitesCan You Prove a New CVE Is Exploitable Before Attackers Do? Learn How in This WebinarCritical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS ZoneAcronis cPanel Backup Plugin Vulnerability Exploited in Targeted AttacksC1b3rwall se arma contra la crisis de ciberseguridad que amenaza la supervivencia de las empresas españolasCarnival promete relax y lujo en sus cruceros; los hackers encontraron además millones de perfiles personalesUn hacker canadiense de 23 años, detenido por operar la botnet KimwolfUn gigante de la logística sufre una brecha de datos de 840 millones de registrosLos ciberdelincuentes ya no respetan ni los carros de la compraThreat Intelligence Alone Won’t Close the Exploitation GapOne Extension Could Hijack AI Assistants Across Chrome, Comet, Edge, Opera Neon and ClaudeThree Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and WipersAttackers Exploit Issabel Framework Flaw Enabling Unauthenticated OS Command ExecutionParallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can’t Install FixAttacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 RepositoriesA New Challenge for Identity SecurityGoogle Patches Pixel Modem Flaw Amid Signs of Limited Targeted ExploitationActive Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin TokensAttackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web ShellsSi pierdes el móvil este verano, haz esto en los primeros cinco minutos para que no vacíen tus cuentasHalluSquatting, el nuevo truco para engañar a los asistentes de IA y colar malware en tu ordenadorUn hacker adolescente piratea el servicio de streaming de Bandai usando ChatGPTUna agencia de EE.UU. pagó un millón de dólares tras casi un mes de negociación con un grupo de ransomwareUn ciberataque deja sin suministro a KFC y obliga a cerrar temporalmente algunos restaurantesKREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session TokensIranian Hackers Use Telegram-Controlled Malware to Spy on Dissidents and JournalistsBambooToken Malware Uses MQTT to Control Windows and Linux SystemsMass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev ServersWhy Testing Individual Techniques Misses the PointHuman Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight SecondsLiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared ServerChina-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGECisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command ExecutionWordPress Adds Automated Plugin Reviews to Block High-Risk Updates Before DistributionTelegram Desktop Flaw Lets Hidden JavaScript Exfiltrate Messages From HTML ExportsPaperCut alerta de ataques activos contra sus programas de gestión de impresorasLas Fuerzas Armadas y la Guardia Civil aceleran su transformación digital ante un ciberespacio cada vez más complejoCuidado con estos anuncios de Facebook: parecen de Google Play, pero conducen a casinos sin licenciaUna filtración revela cómo Rusia ha creado una cantera universitaria para sus ciberoperaciones militaresUn fallo en Lenovo ID permite el acceso sin autorización a unas 5.000 cuentas de Dropbox3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber CredentialsRed Heron Exploits Gitea RCE to Compromise 13 Organizations Across Six CountriesNew DDRop Attack Breaks Intel TDX and AMD SEV-SNP Confidential ComputingRogue AI Agents, WeChat Worm, PaperCut Attacks, AI Espionage, and RootkitsAI Changed the Exposure Problem. Validation Needs to Change With It.Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 UsersAttackers Use Passkey Phishing to Hijack Microsoft Cloud Accounts and Exfiltrate DataCISA Adds 5 Actively Exploited Artifactory, ScreenConnect, and RouterOS Flaws to KEVWhat It Does to Your SOCOpenAI Agents Linked to RubyGems Campaign That Gained RCE on RubyDoc ServersAnthropic Says Seven China-Based AI Labs Ran Industrial-Scale Claude Distillation AttacksGitLab CVSS 10 File-Read Flaw Draws In-the-Wild Probes After DisclosureRussian State-Sponsored Hackers Use Claude to Rebuild Malware After DetectionClaude Used to Automate Exploitation and Data Theft Across Multiple VictimsYour Critical Vulnerabilities Might Not Be Your Biggest RiskCisco FMC Flaws Exploited to Steal Credentials and Deploy Qilin RansomwarePaperCut Replaces Emergency Patches With Fixes for Two Actively Exploited FlawsChina-Linked UNC3569 Exploited Sogou Input Method Flaw to Deploy GRAYRABBIT BackdoorAttackers Chain JFrog Artifactory Flaws to Gain Admin Control and Plant Backdoors200 Android Flaws, Browser-Built Phishing, 119K Scam Shops + 23 More StoriesGigabud Creates Android Work Profiles to Hide From Banking App Malware ChecksGoogle Play Early Access Abused to Push Thousands of Deceptive Android AppsPaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ InstancesCheck Point Discloses Two 9.8-Rated VPN Certificate Flaws Enabling Unauthenticated RCECISA Flags Exploited Cisco, Citrix, Fortinet Flaws, Sets Sept. 12 Federal Patch DeadlineAnthropic Discloses Fourth AI Hacking Incident Involving Claude Opus 4.6Nearly 1 in 10 Exposed LiteLLM Gateways Accepted the Example «sk-1234» Admin KeyFour Spy Groups Used the Same Chrome and Windows Exploit Kit Within a WeekU.S. Disrupts Xinbi Guarantee Scam Marketplace, Freezes $52.8 Million in CryptoSAP Patches CVSS 10.0 Kernel Flaw Enabling Unauthenticated Remote Code ExecutionResearcher Drops New Microsoft Defender PoC Showing ShieldBreak Patch Can Be BypassedF5 BIG-IP APM Malware Injects a PHP Web Shell Into Memory, Evading Disk ScansU.S. Agencies Accuse China AI Firms of Distilling Claude, GPT, Gemini, and GrokInfostealer Logs Expose Replayable AI Tokens That Can Bypass MFALearn How to Answer “Are We Exposed?” Faster After a New CVEAlby Hub Critical Flaw Could Let Attackers Take Over Internet-Exposed Bitcoin WalletsDeepSeek Harness Flaw Let AI Agents Disable Their Own File Sandbox Without ApprovalNew cPanel Flaw Lets a Hosting Account With Mail Privileges Run Code as RootChrome V8 Zero-Day Exploited in the Wild Enables Code Execution Inside SandboxMicrosoft Patches Record 974 Flaws, Including Two Exploited Windows Zero-DaysN-able N-central Pre-Auth RCE Flaw Exploited in the WildAutonomous AI Agents Compromise Thousands of Credentials in Under Six HoursChatGPT Flaw Let a Planted Prompt Send a Victim’s Gmail Data to Another AccountSlim Spider Steals Crypto Custody Secrets From Brazilian Financial InstitutionLiquid Hackers Return 3,400 Bitcoin Taken via Elements Bug, Still Holding $47M in BTCWhat It Took to Reach 1 Billion Build ManifestsWeChat Zero-Click Worm Took Over Accounts on iPhone and Android via Incoming CallsBengalSEO Poisons Bing Search Results to Deliver MayaBot and Tech Support ScamsFreeIPA Flaw Chain Lets Anonymous Clients Create Reusable Administrator Credentials
Chicago 12, Melborne City, USA
  • Home
  • Blog
  • Sample Page
The Digital Fortress
  • Get Started

Etiqueta Developer

  1. Inicio
  2. Open VSX Removes 77 Malicious Evil Twin Extensions Exfiltrating Developer Data
Open VSX Removes 77 Malicious Evil Twin Extensions Exfiltrating Developer Data
  • adminadmin
  • Data
  • Developer
  • agosto 5, 2026
  • 0 Comentarios
Open VSX Removes 77 Malicious Evil Twin Extensions Exfiltrating Developer Data

A cluster of 77 extensions on the Open VSX marketplace has been found to impersonate legitimate developer tools while transmitting information about the systems and development environments on which they…

Continue reading
SleeperGem Uses Three Malicious RubyGems Packages to Target Developer Machines
  • adminadmin
  • Developer
  • Machines
  • julio 20, 2026
  • 0 Comentarios
SleeperGem Uses Three Malicious RubyGems Packages to Target Developer Machines

Cybersecurity researchers have flagged a new software supply chain attack codenamed SleeperGem targeting the Ruby ecosystem after three malicious gems were published to RubyGems with the end goal of serving…

Continue reading
North Korea-Linked npm Packages Mimic Rollup Polyfills to Steal Developer Secrets
  • adminadmin
  • Developer
  • KoreaLinked
  • julio 3, 2026
  • 0 Comentarios
North Korea-Linked npm Packages Mimic Rollup Polyfills to Steal Developer Secrets

Threat actors with ties to North Korea have been linked to a fresh set of malicious npm packages that masquerade as Rollup polyfill tooling to facilitate remote access and data…

Continue reading
Amazon Q Developer Flaw Could Let Malicious Repos Run Code via MCP Configs
  • adminadmin
  • Amazon
  • Code
  • junio 26, 2026
  • 0 Comentarios
Amazon Q Developer Flaw Could Let Malicious Repos Run Code via MCP Configs

Swati KhandelwalJun 26, 2026AI Security / Vulnerability A high-severity flaw in Amazon Q Developer let a malicious repository run commands and steal a developer’s cloud credentials. The path was short:…

Continue reading
Google Sets Sept. 30 Deadline for Android Developer Verification in Four Countries
  • adminadmin
  • Android
  • Countries
  • junio 22, 2026
  • 0 Comentarios
Google Sets Sept. 30 Deadline for Android Developer Verification in Four Countries

Swati KhandelwalJun 22, 2026Mobile Security / Open Source Google has set September 30, 2026, as the day it begins enforcing Android developer verification in the first four countries, and the major device-maker…

Continue reading
North Korean Hackers Are Turning Developer Tools Into Malware Delivery Channels
  • adminadmin
  • Channels
  • Delivery
  • junio 15, 2026
  • 0 Comentarios
North Korean Hackers Are Turning Developer Tools Into Malware Delivery Channels

Cybersecurity researchers have flagged two malicious cyber campaigns that exhibit similarities with a persistent North Korean threat cluster known as Contagious Interview (aka Famous Chollima, HexagonalRodent, and Void Dokkaebi). According…

Continue reading
GlassWorm Malware Takedown Disrupts Developer Supply Chain Attack Infrastructure
  • adminadmin
  • Attack
  • Chain
  • mayo 27, 2026
  • 0 Comentarios
GlassWorm Malware Takedown Disrupts Developer Supply Chain Attack Infrastructure

Ravie LakshmananMay 27, 2026Malware / Threat Intelligence CrowdStrike, in partnership with Google and the Shadowserver Foundation, has announced the simultaneous disruption of all command-and-control (C2) channels associated with GlassWorm, a…

Continue reading
Developer Workstations Are Now Part of the Software Supply Chain
  • adminadmin
  • Chain
  • Developer
  • mayo 18, 2026
  • 0 Comentarios
Developer Workstations Are Now Part of the Software Supply Chain

Supply chain attackers are not only trying to slip malicious code into trusted software. They are trying to steal the access that makes trusted software possible. Recently, three separate campaigns…

Continue reading
Stealer Backdoor Found in 3 Node-IPC Versions Targeting Developer Secrets
  • adminadmin
  • Backdoor
  • Developer
  • mayo 14, 2026
  • 0 Comentarios
Stealer Backdoor Found in 3 Node-IPC Versions Targeting Developer Secrets

Cybersecurity researchers are sounding the alarm about what has been described as «malicious activity» in newly published versions of node-ipc. According to Socket and StepSecurity, three different versions of the…

Continue reading
Quasar Linux RAT Steals Developer Credentials for Software Supply Chain Compromise
  • adminadmin
  • Chain
  • Compromise
  • mayo 8, 2026
  • 0 Comentarios
Quasar Linux RAT Steals Developer Credentials for Software Supply Chain Compromise

Ravie LakshmananMay 08, 2026Linux / DevOps A previously undocumented Linux implant codenamed Quasar Linux RAT (QLNX) is targeting developers’ systems to establish a silent foothold as well as facilitate a…

Continue reading

Paginación de entradas

1 2

Recent Posts

  • U.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS Attacks
  • Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks
  • Gyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata Records
  • Un ciberataque contra Inditex afecta a sus bases de datos internas
  • Hackean a una empresa de ciberseguridad y exponen datos y cámaras de clientes

Recent Comments

No hay comentarios que mostrar.

Archives

  • septiembre 2026
  • agosto 2026
  • julio 2026
  • junio 2026
  • mayo 2026
  • abril 2026
  • marzo 2026
  • febrero 2026
  • agosto 2024

Categories

  • Uncategorized

Other Story

Uncategorized

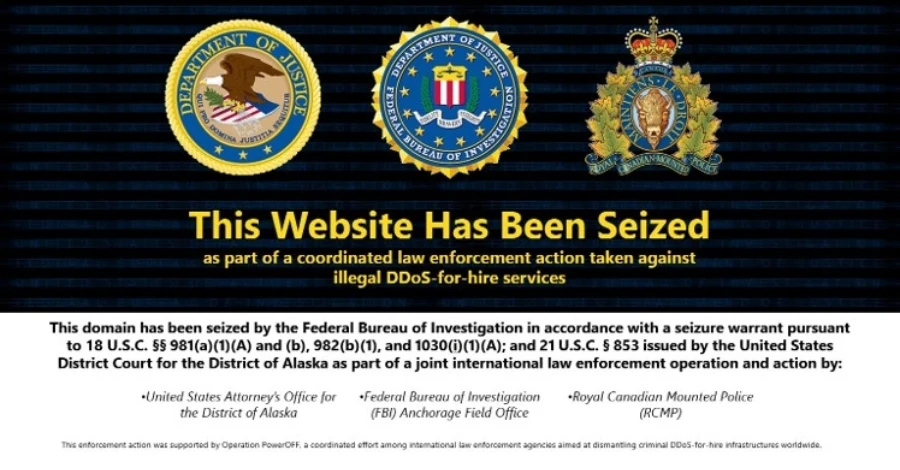
U.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS Attacks

  • admin
  • septiembre 17, 2026
U.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS Attacks
Uncategorized

Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks

  • admin
  • septiembre 17, 2026
Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks
Uncategorized

Gyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata Records

  • admin
  • septiembre 17, 2026
Gyazo Breach Exposes 23.62 Million User Records and 490 Million Image Metadata Records
Uncategorized

Un ciberataque contra Inditex afecta a sus bases de datos internas

  • admin
  • septiembre 17, 2026
Un ciberataque contra Inditex afecta a sus bases de datos internas
Uncategorized

Hackean a una empresa de ciberseguridad y exponen datos y cámaras de clientes

  • admin
  • septiembre 17, 2026
Hackean a una empresa de ciberseguridad y exponen datos y cámaras de clientes
Uncategorized

Los datos de los funcionarios del Palacio Real de Marruecos, en manos de un hacker

  • admin
  • septiembre 17, 2026
Los datos de los funcionarios del Palacio Real de Marruecos, en manos de un hacker
Copyright © 2026 The Digital Fortress | Powered by Desert Themes
Back to Top