FreeIPA Flaw Chain Lets Anonymous Clients Create Reusable Administrator Credentials
A flaw in FreeIPA lets a client that has never logged in create a Kerberos identity of its own choosing in the directory and end up in the administrators group,…
Ravie LakshmananSep 08, 2026Vulnerability / Web Security Adobe on Monday released security patches to address a maximum-severity flaw impacting Adobe Commerce and Magento Open Source that has come under active exploitation in…
Ravie LakshmananSep 08, 2026Data Privacy / Regulation Online dating app Grindr has opted to pay £26 million ($35.1 million) to settle a lawsuit in the U.K. over allegations that it…
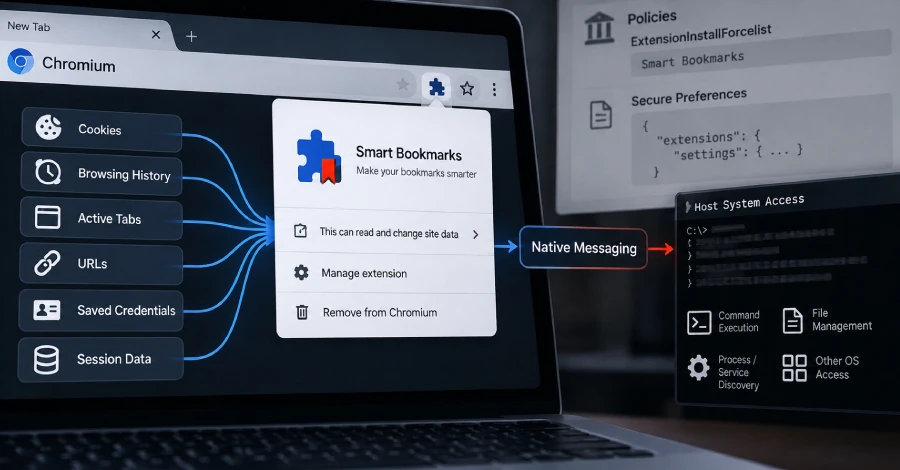
Cybersecurity researchers have disclosed details of a complex Chromium-based post-exploitation toolkit called PEEP that masquerades as a bookmarks extension for the web browser. «Requiring prior administrative or code execution access,…
Turning off email images should at least stop the pictures. This week, attackers had a workaround: a scannable QR code built out of text. It still appears, even with images…
Ravie LakshmananSep 07, 2026Phishing / Identity Security Threat hunters have disclosed details of a widespread data theft and extortion threat cluster that’s targeting Microsoft 365 and other software-as-a-service (SaaS) offerings…
A TantoSec proof-of-concept turns an AES-CBC «padding oracle» in Telerik UI for ASP.NET AJAX into unauthenticated remote code execution — but only against applications in a specific non-default configuration, and…
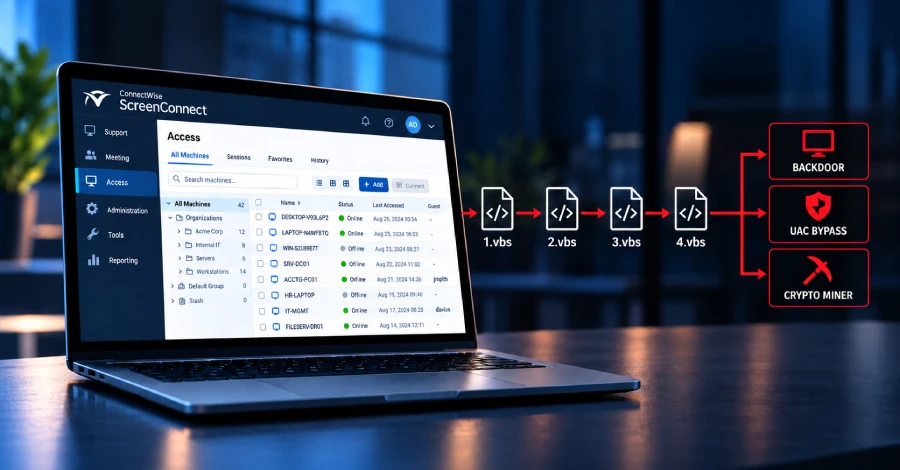
Ravie LakshmananSep 07, 2026Malware / Vulnerability Cybersecurity researchers have disclosed details of worm-like activity that abuses ConnectWise ScreenConnect to distribute a malicious Visual Basic Script (VBScript) payload to newly connected…
If managing security across multiple cloud providers wasn’t hard enough, each one fails in a different way. For the 2026 Cloud Security Index, Intruder analyzed misconfiguration data from 3,000 organizations…
Every on-premises N-central build below 2026.3.1.14 — including servers updated to Hotfix 3 a day earlier — needs Hotfix 4. N-able’s incident notice says the flaw has been exploited in…