admin
Chrome 0-Day, Router Hijacks, Coder Supply Chain Attack and More
Turning off email images should at least stop the pictures. This week, attackers had a workaround: a scannable QR code built out of text. It still appears, even with images…
Turning off email images should at least stop the pictures. This week, attackers had a workaround: a scannable QR code built out of text. It still appears, even with images…
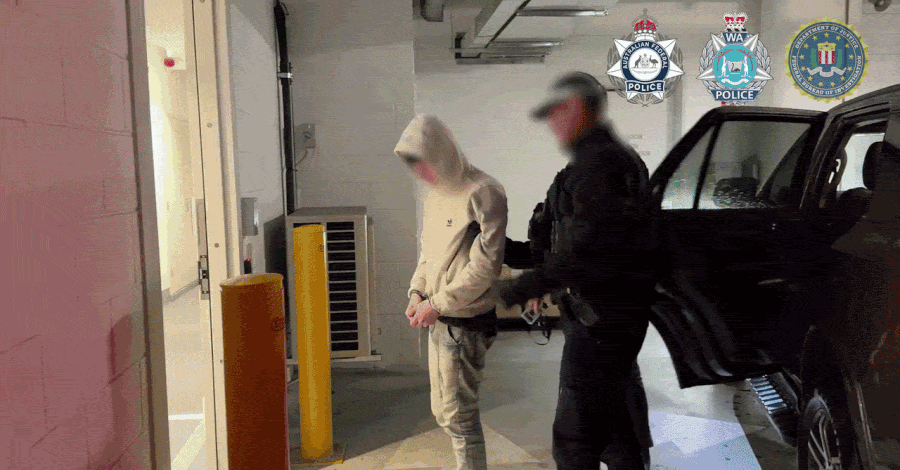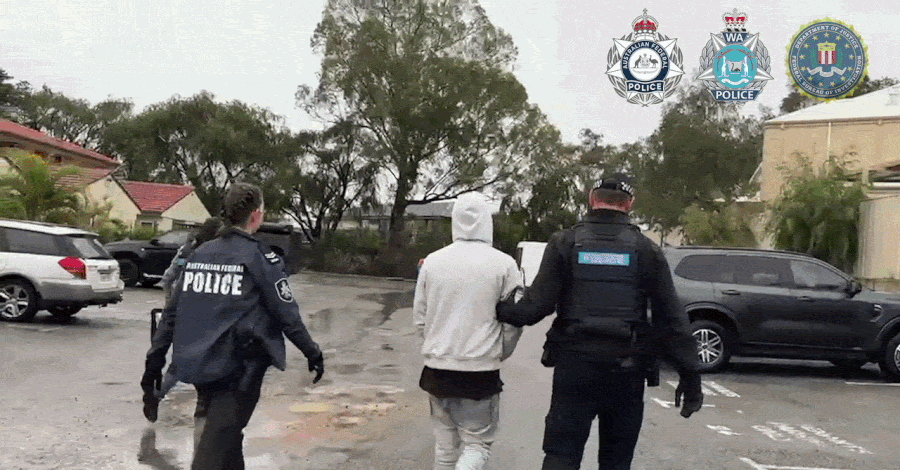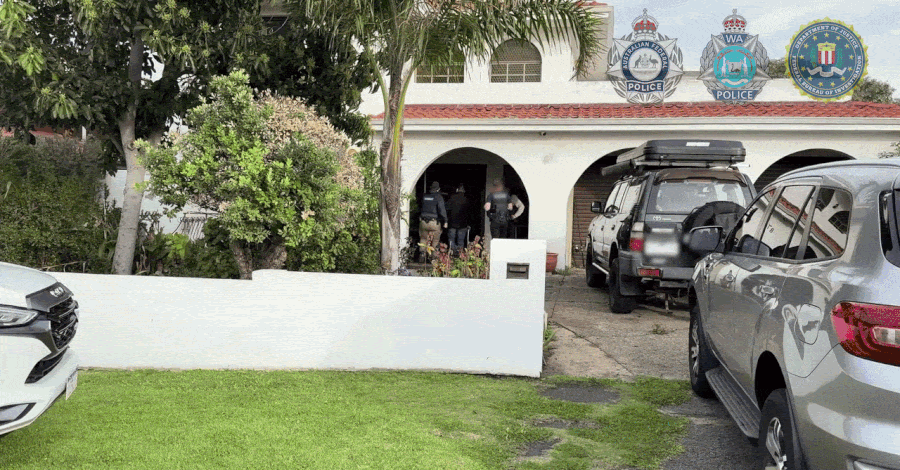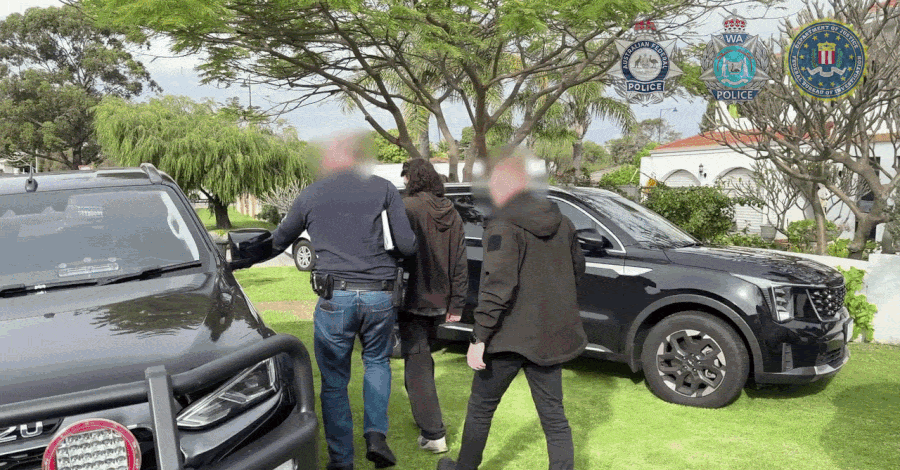
The Australian Federal Police (AFP) has charged two Western Australian men with a combined total of 14 offences over their alleged role in TeamPCP, the cybercrime group behind the March…
The Rust Project has deleted malicious versions of three widely used Rust crates from crates.io after a compromised maintainer account published releases that added a typosquatted dependency whose build script…

Ravie LakshmananAug 11, 2026Supply Chain Attack / Vulnerability Cybersecurity researchers have warned of a supply chain compromise impacting WordPress plugin vendor BdThemes, prompting the content management systems (CMS) platform’s plugins…
Ravie LakshmananAug 07, 2026Cybercrime / Vulnerability A new analysis has uncovered that the threat actor tracked as TeamPCP has been active on the cybercrime scene as far back as 2020,…

Cybersecurity researchers have disclosed what has been described as a «long-standing supply chain attack» on QuickFox, a virtual private network (VPN) and network acceleration tool designed for overseas Chinese users.…

Ravie LakshmananJul 09, 2026Supply Chain Security / DevSecOps GitHub has officially announced the release of npm version 12 with install scripts disabled by default, along with deprecating granular access tokens…

The Hacker NewsJul 07, 2026AI Security / Software Supply Chain Software supply chain security was hard enough. Then AI joined the build pipeline. For five years, «software supply chain security»…

Threat actors associated with the Anubis ransomware operation have been observed exploiting the Citrix Bleed 2 (CVE-2025-5777) vulnerability to obtain initial access. «Although tactics differ between affiliates, common patterns emerged…

Cybersecurity researchers have flagged yet another evolution of the supply chain attack linked to the Mini Shai-Hulud, Miasma, and Hades malware family that has compromised a new set of npm…