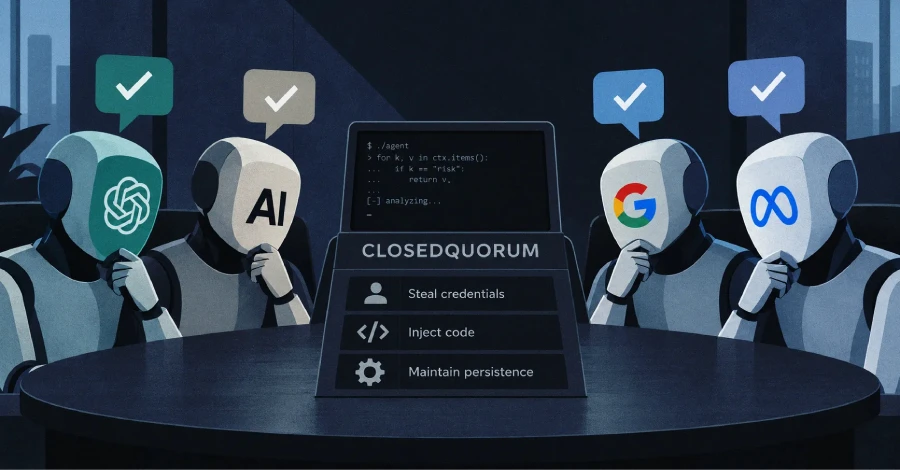
This Windows Malware is Built to Let Up to Four AI Models Vote on Its Next Move
A Windows malware called CLOSEDQUORUM is built to take orders from a vote of up to four AI models instead of an attacker’s server, Cisco Talos said on September 22.…
A Windows malware called CLOSEDQUORUM is built to take orders from a vote of up to four AI models instead of an attacker’s server, Cisco Talos said on September 22.…
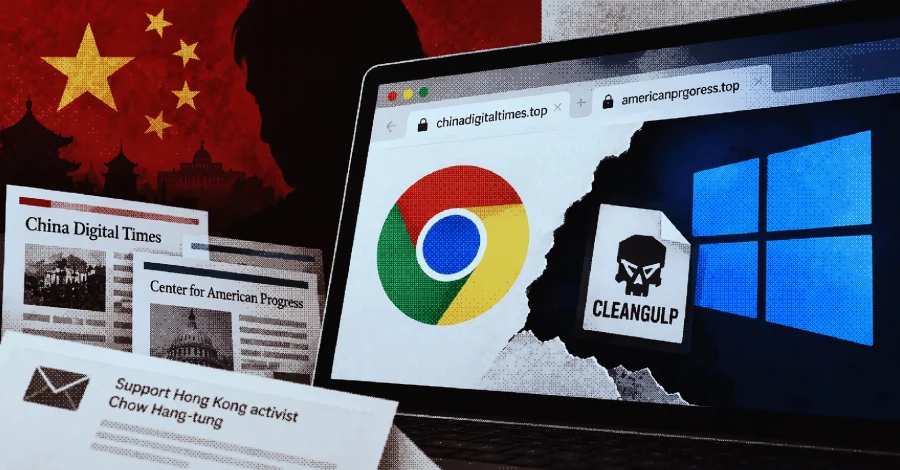
Ravie LakshmananSep 23, 2026Zero-Day / Vulnerability A Chinese threat actor codenamed UTA0565 has been observed exploiting the recently disclosed Google Chrome-Microsoft Windows exploit chain as zero-days through fake websites. The…

Ravie LakshmananSep 18, 2026Mobile Security / Malware Cybersecurity researchers have flagged a new Android malware called RatHat that’s assessed to be operated by China-based threat actors and features an artificial…
Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the activity under the moniker REF9334.…
 admin
Cybersecurity agencies in the United States, the United Kingdom, and the Netherlands have detailed a Windows malware that they say Iran’s intelligence service uses to spy on dissidents, journalists, and…
 admin
Cybersecurity researchers have disclosed details of a multi-platform campaign that uses the Message Queueing Telemetry Transport (MQTT) protocol as a communication channel to control Windows and Linux systems. The emerging…

Anthropic on Thursday revealed it disrupted a campaign mounted by a Russian state-sponsored threat actor that abused Claude for developing an AI-assisted workflow to get ahead of the detection curve.…

The Gigabud banking trojan now installs a second Android app that creates a work profile on an infected phone and drops a tampered banking app inside it, security firm Group-IB…

Malware linked to break-ins at F5 BIG-IP Access Policy Manager appliances hides a PHP web shell in memory instead of in a file on disk, Sophos said in an analysis…
 admin
Cybersecurity researchers have unpacked JSCeal, a sophisticated compiled V8 JavaScript (JSC) malware with credential harvesting, surveillance, and traffic-interception capabilities. «The payloads are protected with javascript-obfuscator, using multiple techniques including RC4-protected…